<< Prev Question Next Question >>
Question 5/7
Build a multi-tier network capable of supporting application virtual machines deployed across multiple vCenter instances.
Requirements:
vCenter: vcsa-01a.corp.local
Credentials: [email protected] / VMware1!
Resource Pools: Management and Edge Cluster 1A
The underlying physical network does not support multicast.
All new items created must have a prefix of "U" followed by their function name and a suffix of "New".
i.e. U-App-Tier-NEW.
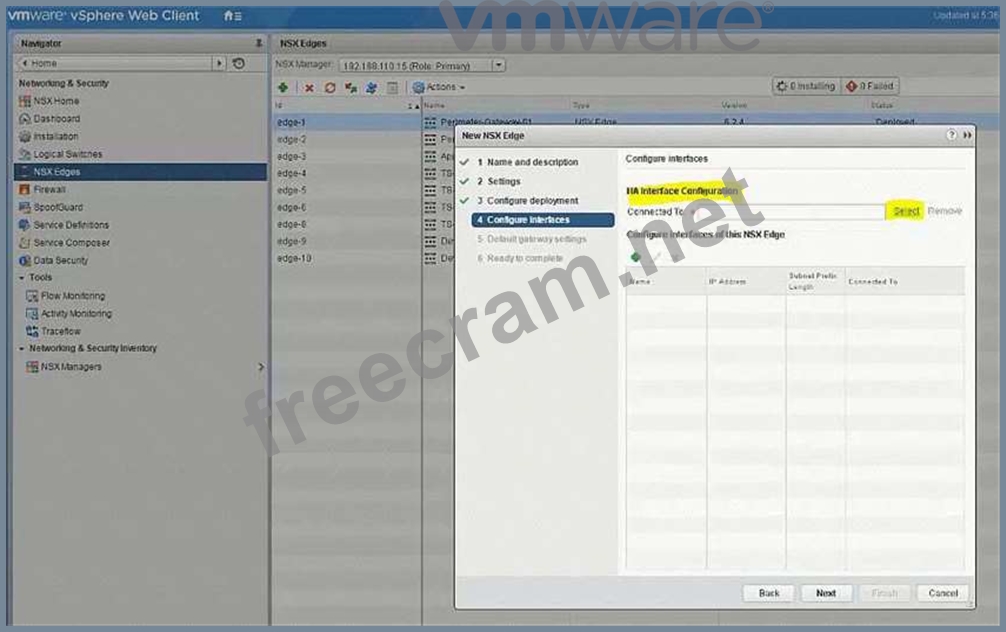
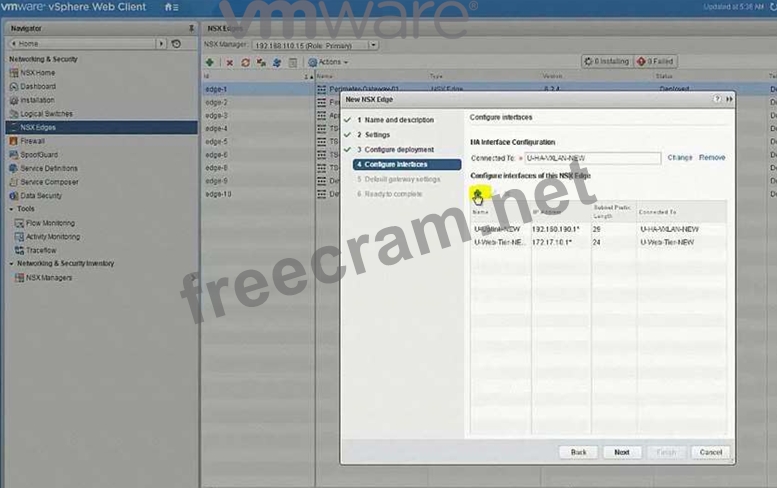
Create a LS for HA management interface calle U-HA-VXLAN=NEW but do not enable HA on any of the edge devices deployed.
Deploy logical switches using separate subnets for the three tier application shared by both NSX Manager instances.
Deploy the required east-west routing component used across multiple vCenter instances for the multi-tier network.
Utilize a default gateway up to the Perimeter-Gateway02 (tenant router) from the east/west router.
Utilize a static route from the tenant router to reach the three tiers of the application.
Subnets for the tiers:
172.7.10.0/24 for the Web Tier.
172.17.20.1/24 for the App Tier.
172.17.30.0/24 for the Database Teir.
Use the first available IP address for the router on each of the tiers.
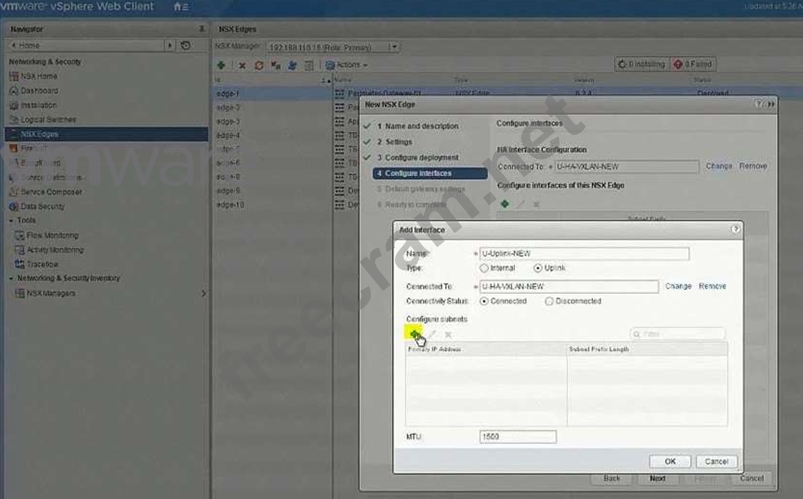
Subnet for the Transit VXLAN uplink from the application tier routing to the tenant router.
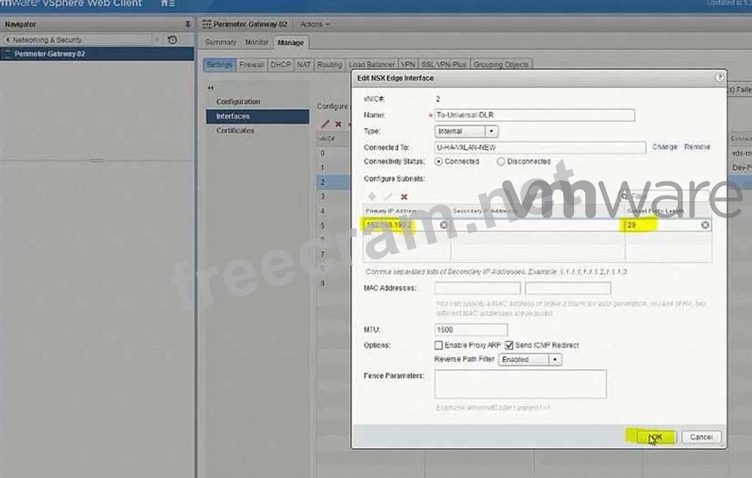
192.168.190.0/29
Uplink IP address of the application tier should be the first available IP address.
Downlink from the tenant router will use the second available IP addresses.
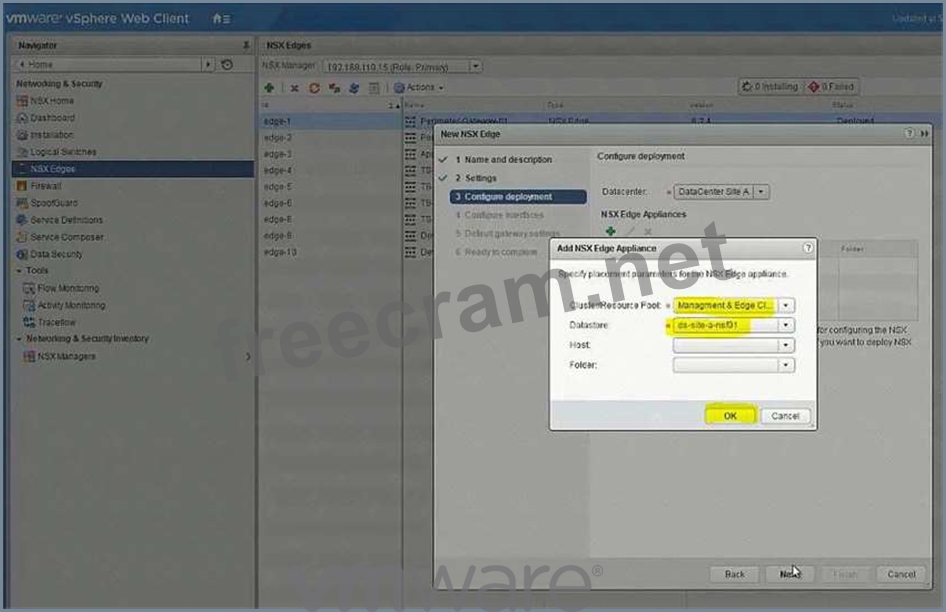
The password for new edge device(s) must be VMware1!VMware1!
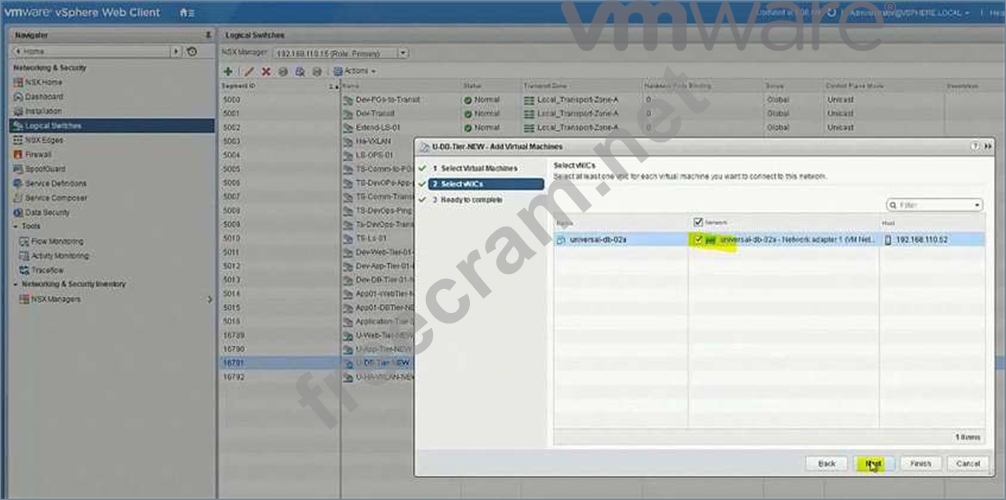
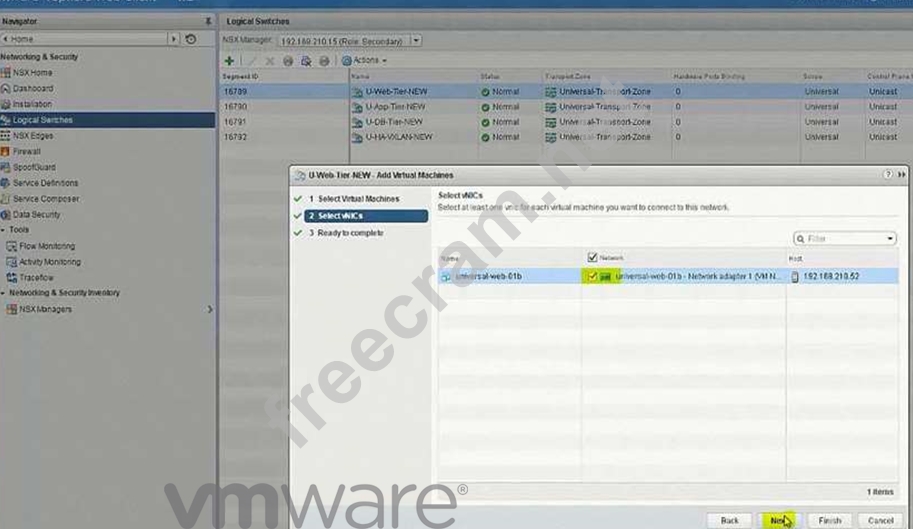
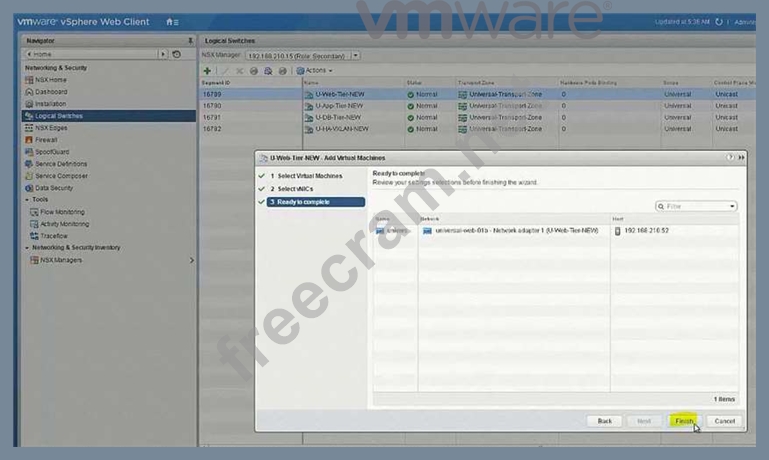
Add all virtual machines with a prefix "universal-" to their respective segments.
Ensure all LIFs are reachable from ControlCenter.
HOL LAB for Practice:
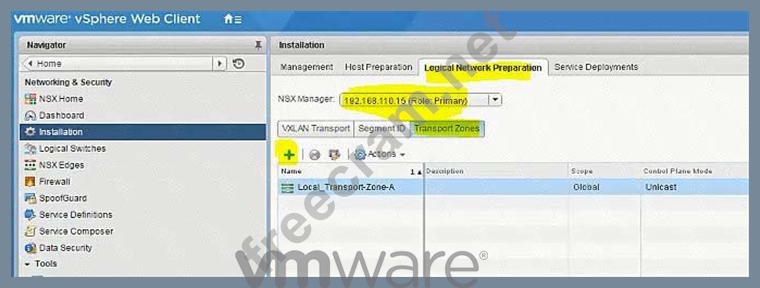
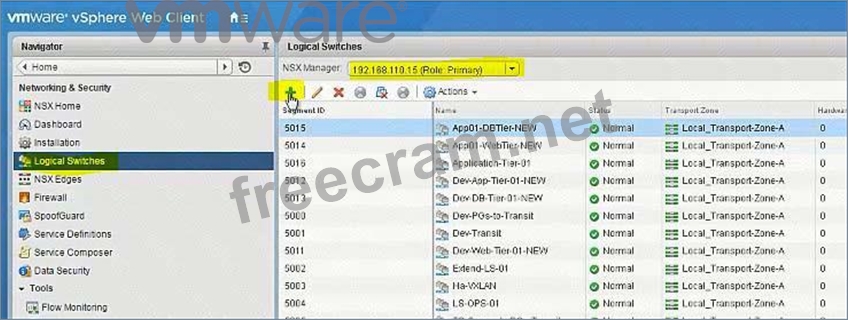
See the explanation part for complete solution.
Requirements:
vCenter: vcsa-01a.corp.local
Credentials: [email protected] / VMware1!
Resource Pools: Management and Edge Cluster 1A
The underlying physical network does not support multicast.
All new items created must have a prefix of "U" followed by their function name and a suffix of "New".
i.e. U-App-Tier-NEW.
Create a LS for HA management interface calle U-HA-VXLAN=NEW but do not enable HA on any of the edge devices deployed.
Deploy logical switches using separate subnets for the three tier application shared by both NSX Manager instances.
Deploy the required east-west routing component used across multiple vCenter instances for the multi-tier network.
Utilize a default gateway up to the Perimeter-Gateway02 (tenant router) from the east/west router.
Utilize a static route from the tenant router to reach the three tiers of the application.
Subnets for the tiers:
172.7.10.0/24 for the Web Tier.
172.17.20.1/24 for the App Tier.
172.17.30.0/24 for the Database Teir.
Use the first available IP address for the router on each of the tiers.
Subnet for the Transit VXLAN uplink from the application tier routing to the tenant router.
192.168.190.0/29
Uplink IP address of the application tier should be the first available IP address.
Downlink from the tenant router will use the second available IP addresses.
The password for new edge device(s) must be VMware1!VMware1!
Add all virtual machines with a prefix "universal-" to their respective segments.
Ensure all LIFs are reachable from ControlCenter.
HOL LAB for Practice:
See the explanation part for complete solution.