- Home
- Splunk
- Splunk Certified Cybersecurity Defense Engineer
- Splunk.SPLK-5002.v2026-11-18.q46
- Question 41
Valid SPLK-5002 Dumps shared by ExamDiscuss.com for Helping Passing SPLK-5002 Exam! ExamDiscuss.com now offer the newest SPLK-5002 exam dumps, the ExamDiscuss.com SPLK-5002 exam questions have been updated and answers have been corrected get the newest ExamDiscuss.com SPLK-5002 dumps with Test Engine here:
Access SPLK-5002 Dumps Premium Version
(108 Q&As Dumps, 35%OFF Special Discount Code: freecram)
<< Prev Question Next Question >>
Question 41/46
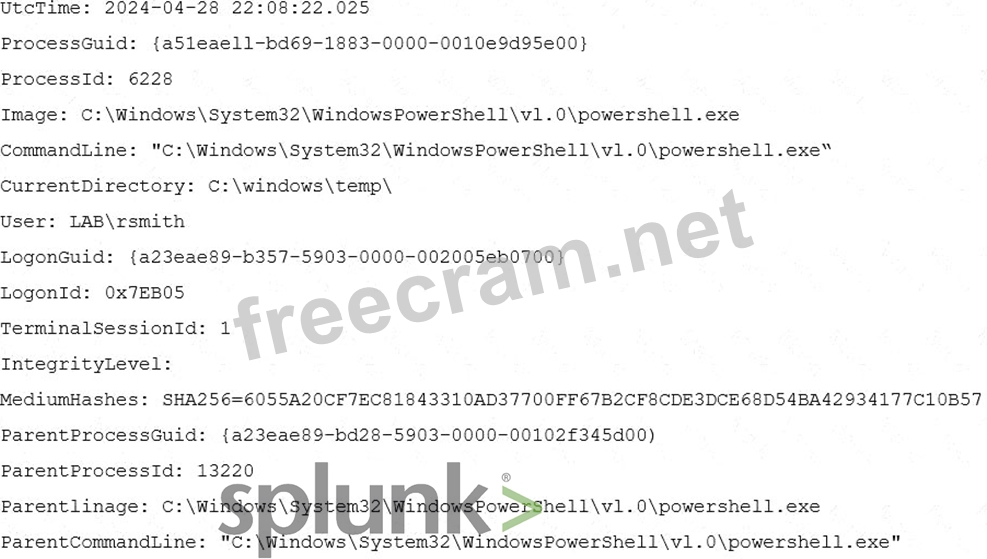
Below is an example of a Sysmon process create log. Which EventCode would be associated with this log entry?
Correct Answer: A
A Sysmon Process Create event is identified by Event ID 1 , making EventCode=1 the correct selection.
This event type is among the most important endpoint telemetry sources for detection engineering because it records process execution and provides fields useful for reconstructing process relationships and identifying suspicious command execution.
Typical Process Create telemetry can contain attributes such as the process image, command line, process identifier, parent process, parent command line, user context, hashes, integrity level, and process GUID.
These fields support detections for suspicious scripting interpreters, unusual parent-child relationships, LOLBins, encoded commands, malware execution, and other endpoint behaviors.
The remaining event IDs represent different Sysmon activities. Event ID 2 concerns changes to file creation time, while Event ID 3 represents network connections when that telemetry is enabled. Event ID 4 records changes in the Sysmon service state. None of those describes the process-creation record shown in the question.
Correct event-type interpretation is fundamental to building accurate SPL because filtering on the wrong EventCode can completely change the semantic meaning of a detection.
Study Guide topics: Sysmon telemetry, Event ID 1, process creation, Windows endpoint data, process analytics, event normalization.
This event type is among the most important endpoint telemetry sources for detection engineering because it records process execution and provides fields useful for reconstructing process relationships and identifying suspicious command execution.
Typical Process Create telemetry can contain attributes such as the process image, command line, process identifier, parent process, parent command line, user context, hashes, integrity level, and process GUID.
These fields support detections for suspicious scripting interpreters, unusual parent-child relationships, LOLBins, encoded commands, malware execution, and other endpoint behaviors.
The remaining event IDs represent different Sysmon activities. Event ID 2 concerns changes to file creation time, while Event ID 3 represents network connections when that telemetry is enabled. Event ID 4 records changes in the Sysmon service state. None of those describes the process-creation record shown in the question.
Correct event-type interpretation is fundamental to building accurate SPL because filtering on the wrong EventCode can completely change the semantic meaning of a detection.
Study Guide topics: Sysmon telemetry, Event ID 1, process creation, Windows endpoint data, process analytics, event normalization.


- Question List (46q)
- Question 1: Consider the following series of events: 4:00 GMT Detection ...
- Question 2: What can an engineer use to capture contextual values from a...
- Question 3: When creating a new playbook to be called directly from Miss...
- Question 4: Which type of correlation search reviews the events in the r...
- Question 5: What is the primary purpose of data indexing in Splunk?...
- Question 6: When creating a detection, how might an engineer ensure that...
- Question 7: In order to perform a complete data assessment, an engineer ...
- Question 8: Which tool can help provide a baseline of the data sources i...
- Question 9: Which REST call will show a list of alerts with their specif...
- Question 10: In Enterprise Security, what is the name of the threat intel...
- Question 11: Which of the following is a reason to utilize ES risk framew...
- Question 12: Which of the following is a methodology to help prevent mali...
- Question 13: Which of the following detections would use a high count of ...
- Question 14: A SOC ' s Incident Response Standard Operating Procedure (SO...
- Question 15: A detection engineer is using a threat defense informed stra...
- Question 16: What does the following search do? source=WinEventLog:securi...
- Question 17: MITRE D3FEND is designed to complement MITRE ' s list of adv...
- Question 18: During a ransomware attack, an adversary might add a default...
- Question 19: What should a security engineer prioritize when building a n...
- Question 20: Which phase of the incident response lifecycle would cause t...
- Question 21: Which of the following can process data from configured cont...
- Question 22: In the context of Splunk ' s Common Information Model (CIM),...
- Question 23: There are multiple methods for communicating data with a RES...
- Question 24: When building detections using the Authentication Data Model...
- Question 25: What is Enterprise Security ' s default way of determining t...
- Question 26: Which practices strengthen the development of Standard Opera...
- Question 27: A cyber defense engineer plays a role in maintaining a secur...
- Question 28: While working with the SOC analysts to review current contex...
- Question 29: How can an engineer verify if results will return for a pote...
- Question 30: Which action improves the effectiveness of notable events in...
- Question 31: Which stats event field created by an adaptive response acti...
- Question 32: How does Mission Control decipher which response template to...
- Question 33: An engineer is writing a correlation search and needs to use...
- Question 34: Which features are crucial for validating integrations in Sp...
- Question 35: Which of the following is the most efficient search to retur...
- Question 36: What document can be helpful in understanding the prioritiza...
- Question 37: Which of the following macro values will exclude all of the ...
- Question 38: What is one method used in ESCU content to calculate a risk ...
- Question 39: A new playbook needs to be developed for automated phishing ...
- Question 40: What must be configured as a setting in a correlation search...
- Question 41: Below is an example of a Sysmon process create log. Which Ev...
- Question 42: In a contextualization playbook, a URL is transmitted to a s...
- Question 43: An engineer has been asked to build a new dashboard after an...
- Question 44: An effective method for building automation workflows is to ...
- Question 45: Risk scores are associated with how many levels of risk in E...
- Question 46: What external support consideration should an engineer accou...
