- Home
- ISC
- Certified Information Systems Security Professional (CISSP)
- ISC.CISSP.v2026-11-14.q747
- Question 590
Valid CISSP Dumps shared by ExamDiscuss.com for Helping Passing CISSP Exam! ExamDiscuss.com now offer the newest CISSP exam dumps, the ExamDiscuss.com CISSP exam questions have been updated and answers have been corrected get the newest ExamDiscuss.com CISSP dumps with Test Engine here:
Access CISSP Dumps Premium Version
(1811 Q&As Dumps, 35%OFF Special Discount Code: freecram)
<< Prev Question Next Question >>
Question 590/747
Drag and Drop Question
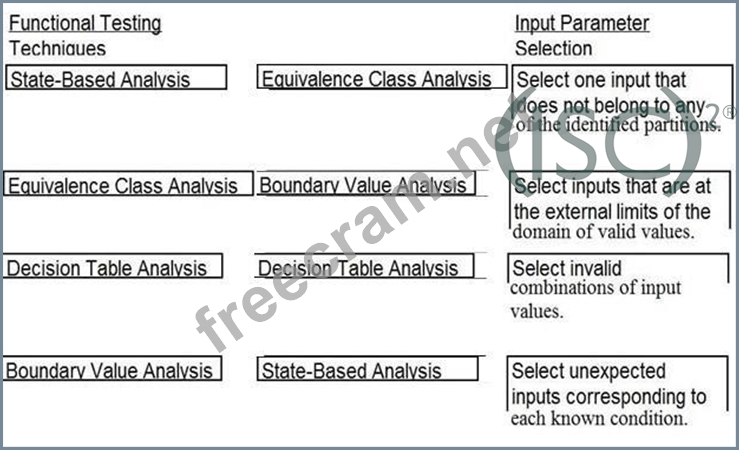
A software security engineer is developing a black box-based test plan that will measure the system's reaction to incorrect or illegal inputs or unexpected operational errors and situations.
Match the functional testing techniques on the left with the correct input parameters on the right.

A software security engineer is developing a black box-based test plan that will measure the system's reaction to incorrect or illegal inputs or unexpected operational errors and situations.
Match the functional testing techniques on the left with the correct input parameters on the right.
Correct Answer:


- Question List (747q)
- Question 1: In a multi-tenant cloud environment, what approach will secu...
- Question 2: Which of the following BEST describes "Privilege Creep"?...
- Question 3: Asymmetric algorithms are used for which of the following wh...
- Question 4: In a financial institution, who has the responsibility for a...
- Question 5: Which of the following techniques BEST prevents buffer overf...
- Question 6: Which of the following BEST describes the purpose of "Egress...
- Question 7: Which service management process BEST helps information tech...
- Question 8: Which of the following BEST describes the purpose of an "Egr...
- Question 9: Which type of control recognizes that a transaction amount i...
- Question 10: Which kind of dependencies should be avoided when implementi...
- Question 11: Which type of test suite should be run for fast feedback dur...
- Question 12: Which of the following BEST describes "steganography"?...
- Question 13: In fault-tolerant systems, what do rollback capabilities per...
- Question 14: Which of the following countermeasures is the MOST effective...
- Question 15: Upon commencement of an audit within an organization, which ...
- Question 16: At the destination host, which of the following OSI model la...
- Question 17: Which of the following protocols will allow the encrypted tr...
- Question 18: Which of the following processes has the PRIMARY purpose of ...
- Question 19: During a penetration test, what are the three PRIMARY object...
- Question 20: Which security evaluation model assesses a product's Securit...
- Question 21: If a content management system (CMC) is implemented, which o...
- Question 22: Single sign-on (SSO) for federated identity management (FIM)...
- Question 23: Which of the following BEST describes the difference between...
- Question 24: Which of the following should exist in order to perform a se...
- Question 25: Which is the second phase of public key Infrastructure (pk1)...
- Question 26: Which of the following is an effective method for avoiding m...
- Question 27: Which of the following BEST describes the objectives of the ...
- Question 28: Which of the following is critical for establishing an initi...
- Question 29: What should be used immediately after a Business Continuity ...
- Question 30: A security professional should ensure that clients support w...
- Question 31: What is the BEST way to encrypt web application communicatio...
- Question 32: What technique BEST describes antivirus software that detect...
- Question 33: A large corporation is locking for a solution to automate ac...
- Question 34: Which of the following entities is ultimately accountable fo...
- Question 35: The key benefits of a signed and encrypted e-mail include...
- Question 36: What is the FINAL step in the waterfall method for contingen...
- Question 37: A security engineer is assigned to work with the patch and v...
- Question 38: What is the MAIN purpose of a security assessment plan?...
- Question 39: Which of the following BEST describes "Public Key Infrastruc...
- Question 40: Which of the following BEST describes the purpose of "saltin...
- Question 41: The development team has been tasked with collecting data fr...
- Question 42: During an audit of system management, auditors find that the...
- Question 43: Which attack defines a piece of code that is inserted into s...
- Question 44: A company is moving from the V model to Agile development. H...
- Question 45: Which technique helps system designers consider potential se...
- Question 46: To prevent inadvertent disclosure of restricted information,...
- Question 47: Which of the following is the MOST important reason for time...
- Question 48: Which of the following BEST describes "Deepfake" technology ...
- Question 49: Which of the following BEST describes the purpose of "Egress...
- Question 50: Which of the following MUST the administrator of a security ...
- Question 51: Data remanence is the biggest threat in which of the followi...
- Question 52: Which of the following BEST describes "Privilege Escalation"...
- Question 53: What is the ultimate objective of information classification...
- Question 54: Reciprocal backup site agreements are considered to be...
- Question 55: A company is attempting to enhance the security of its user ...
- Question 56: Who is the BEST person to review developed application code ...
- Question 57: For privacy protected data, which of the following roles has...
- Question 58: While dealing with the consequences of a security incident, ...
- Question 59: The Hardware Abstraction Layer (HAL) is implemented in the...
- Question 60: Which type of testing evaluates an application's source code...
- Question 61: Which of the following is a strategy of grouping requirement...
- Question 62: What is the MINIMUM standard for testing a disaster recovery...
- Question 63: A system developer has a requirement for an application to c...
- Question 64: Which change management role is responsible for the overall ...
- Question 65: In what phase of the System Development Life Cycle (SDLC) sh...
- Question 66: Discretionary Access Control (DAC) is based on which of the ...
- Question 67: Which of the following is the BEST method a security practit...
- Question 68: Which of the following is a benefit in implementing an enter...
- Question 69: What is the PRIMARY advantage of using automated application...
- Question 70: Which of the following ensures old log data is not overwritt...
- Question 71: Which of the following BEST describes the term "attack surfa...
- Question 72: Which of the following is the BEST way to protect privileged...
- Question 73: Which of the following is used to detect steganography?...
- Question 74: Assuming an individual has taken all of the steps to keep th...
- Question 75: An organization has discovered that users are visiting unaut...
- Question 76: Which of the following access control mechanisms characteriz...
- Question 77: Which of the following BEST describes "Rule-Based Access Con...
- Question 78: A security practitioner needs to implementation solution to ...
- Question 79: Which security action should be taken FIRST when computer pe...
- Question 80: Which of the following BEST describes "Security Debt" in the...
- Question 81: Physical assets defined in an organization's Business Impact...
- Question 82: Which of the following roles is responsible for ensuring tha...
- Question 83: What Is the FIRST step for a digital investigator to perform...
- Question 84: Refer to the information below to answer the question. An or...
- Question 85: A security professional has just completed their organizatio...
- Question 86: Sensitive customer data is going to be added to a database. ...
- Question 87: What is the MOST common security risk of a mobile device?...
- Question 88: The BEST example of the concept of "something that a user ha...
- Question 89: An organization wants to ensure that a message was not alter...
- Question 90: Which of the following BEST describes the purpose of "Egress...
- Question 91: Which of the following actions should be performed when impl...
- Question 92: Which of the following events prompts a review of the disast...
- Question 93: Which of the following BEST describes the purpose of "Egress...
- Question 94: An organization is looking to include mobile devices in its ...
- Question 95: What is the BEST design for securing physical perimeter prot...
- Question 96: What is the BEST approach to addressing security issues in l...
- Question 97: When constructing an Information Protection Policy (IPP), it...
- Question 98: An organization needs a general purpose document to prove th...
- Question 99: Which of the following is a BEST practice when traveling int...
- Question 100: Which of the following four iterative steps are conducted on...
- Question 101: Which of the following BEST describes the purpose of "Egress...
- Question 102: At which phase of the software assurance life cycle should r...
- Question 103: Transport Layer Security (TLS) provides which of the followi...
- Question 104: What is the MOST effective method for gaining unauthorized a...
- Question 105: Which of the following would qualify as an exception to the ...
- Question 106: Which event magnitude is defined as deadly, destructive, and...
- Question 107: Which technique can be used to make an encryption scheme mor...
- Question 108: An organization wants to migrate to Session Initiation Proto...
- Question 109: Which of the following BEST describes "Separation of Duties"...
- Question 110: Which of the following is the MOST challenging issue in appr...
- Question 111: A network administrator is designing a new datacenter in a d...
- Question 112: A security practitioner has been tasked with establishing or...
- Question 113: An organization's information security strategic plan MUST b...
- Question 114: Refer to the information below to answer the question. A new...
- Question 115: A security professional is assessing the risk in an applicat...
- Question 116: Multi-Factor Authentication (MFA) is necessary in many syste...
- Question 117: Which of the following BEST describes "Passwordless Authenti...
- Question 118: Which of the following is used to support the of defense in ...
- Question 119: Which of the following is an initial consideration when deve...
- Question 120: Refer to the information below to answer the question. In a ...
- Question 121: When building a data center, site location and construction ...
- Question 122: An external attacker has compromised an organization's netwo...
- Question 123: How should an organization determine the priority of its rem...
- Question 124: After following the processes defined within the change mana...
- Question 125: Why might a network administrator choose distributed virtual...
- Question 126: A user downloads a file from the Internet, then applies the ...
- Question 127: What should be used to determine the risks associated with u...
- Question 128: Which of the following access control models is MOST restric...
- Question 129: Which of the following BEST describes "spoofing" as an attac...
- Question 130: Refer to the information below to answer the question. A sec...
- Question 131: Which of the following BEST describes a "Distributed Denial ...
- Question 132: Which of the following regulations dictates how data breache...
- Question 133: Which of the following BEST describes "Confusion and Diffusi...
- Question 134: Which of the following vulnerability assessment activities B...
- Question 135: A developer is creating an application that requires secure ...
- Question 136: Which one of the following transmission media is MOST effect...
- Question 137: Which of the following methods provides the MOST protection ...
- Question 138: What should happen when an emergency change to a system must...
- Question 139: What operations role is responsible for protecting the enter...
- Question 140: Which of the following MUST be in place to recognize a syste...
- Question 141: Which of the following BEST describes "Race Condition" vulne...
- Question 142: Drag and Drop Question In which order, from MOST to LEAST im...
- Question 143: A control to protect from a Denial-of-Service (DoS) attach h...
- Question 144: When designing a Cyber-Physical System (CPS), which of the f...
- Question 145: Which one of the following is a threat related to the use of...
- Question 146: Which of the following BEST describes "Supply Chain Risk Man...
- Question 147: Which of the following are all elements of a disaster recove...
- Question 148: Which one of the following considerations has the LEAST impa...
- Question 149: Which of the following BEST describes the purpose of "Egress...
- Question 150: A large bank deploys hardware tokens to all customers that u...
- Question 151: The Open Web Application Security Project's (OWASP) Software...
- Question 152: Which of the following techniques evaluates the secure desig...
- Question 153: An organization has implemented a new backup process which p...
- Question 154: Change management policies and procedures belong to which of...
- Question 155: Which disaster recovery site option provides fully configure...
- Question 156: Which of the following secure startup mechanisms are PRIMARI...
- Question 157: Which of the following BEST describes "Business Email Compro...
- Question 158: Which of the following types of technologies would be the MO...
- Question 159: Why are packet filtering routers used in low-risk environmen...
- Question 160: Which of the following is the MOST effective method of detec...
- Question 161: What is the MOST effective way to protect privacy?...
- Question 162: Which of the following in the BEST way to reduce the impact ...
- Question 163: Which of the following uses the destination IP address to fo...
- Question 164: Which of the following is the MOST important consideration i...
- Question 165: What is the foundation of cryptographic functions?...
- Question 166: Which of the following BEST describes "IPsec Transport Mode"...
- Question 167: Which of the following BEST describes "Kerberos" as an authe...
- Question 168: A federal agency has hired an auditor to perform penetration...
- Question 169: How can an attacker exploit overflow to execute arbitrary co...
- Question 170: Which of the following system components enforces access con...
- Question 171: How does identity as a service (IDaaS) provide an easy mecha...
- Question 172: Which of the following problems is not addressed by using OA...
- Question 173: Users require access rights that allow them to view the aver...
- Question 174: Who must approve modifications to an organization's producti...
- Question 175: One of Canada's leading pharmaceutical firms recently hired ...
- Question 176: If an attacker in a SYN flood attack uses someone else's val...
- Question 177: When implementing controls in a heterogeneous end-point netw...
- Question 178: Information security metrics provide the GREATEST value tp m...
- Question 179: Which of the following goals represents a modern shift in ri...
- Question 180: Which of the following factors should be considered characte...
- Question 181: Which type of firewall makes filtering decisions based on th...
- Question 182: What is the second step in the identity and access provision...
- Question 183: In a basic SYN flood attack, what is the attacker attempting...
- Question 184: What would be the PRIMARY concern when designing and coordin...
- Question 185: Which of the following is a common measure within a Local Ar...
- Question 186: Which of the following measures serves as the BEST means for...
- Question 187: Activity to baseline, tailor, and scope security controls ti...
- Question 188: What is the FIRST step in risk management?...
- Question 189: Which of the following mandates the amount and complexity of...
- Question 190: Secure real-time transport protocol (SRTP) provides security...
- Question 191: Which of the following addresses requirements of security as...
- Question 192: In order for a security policy to be effective within an org...
- Question 193: Access to which of the following is required to validate web...
- Question 194: Which of the following Disaster recovery (DR) testing proces...
- Question 195: What are the first two components of logical access control?...
- Question 196: When conducting a remote access session using Internet Proto...
- Question 197: Why should Open Web Application Security Project (OWASP) App...
- Question 198: Which of the following is MOST important when assigning owne...
- Question 199: A company needs to provide employee access to travel service...
- Question 200: Which one of the following security mechanisms provides the ...
- Question 201: An organization regularly conducts its own penetration tests...
- Question 202: An organization recently conducted a review of the security ...
- Question 203: Which of the following BEST describes "Container Security" c...
- Question 204: Which of the following is an example of a "compensating cont...
- Question 205: Which of the following measures is the MOST critical in orde...
- Question 206: Utilizing a public wireless Local Area network (WLAN) to con...
- Question 207: Including a Trusted Platform Module (TPM) in the design of a...
- Question 208: Which of the following BEST describes how access to a system...
- Question 209: Which of the following BEST describes "Software Bill of Mate...
- Question 210: Which of the following is held accountable for the risk to o...
- Question 211: A disadvantage of an application filtering firewall is that ...
- Question 212: Which of the following is the PRIMARY purpose of a Non-Discl...
- Question 213: Which of the following is a function of Security Assertion M...
- Question 214: Which of the following BEST describes the purpose of a Secur...
- Question 215: At a MINIMUM, audits of permissions to individual or group a...
- Question 216: Which of the following BEST describes the purpose of "Egress...
- Question 217: A security professional was tasked with rebuilding a company...
- Question 218: Which of the following BEST describes "Single Sign-On (SSO)"...
- Question 219: When designing on Occupent Emergency plan (OEP) for United s...
- Question 220: Which of the following BEST describes "Digital Sovereignty" ...
- Question 221: Which of the following needs to be taken into account when a...
- Question 222: Which of the following is the BEST approach to implement mul...
- Question 223: Which of the following is the BEST identity-as-a-service (ID...
- Question 224: Which of the following BEST describes "Business Continuity P...
- Question 225: A web application requires users to register before they can...
- Question 226: Which of the following media is LEAST problematic with data ...
- Question 227: Refer to the information below to answer the question. A sec...
- Question 228: Which of the following BEST describes a "false positive" in ...
- Question 229: While impersonating an Information Security Officer (ISO), a...
- Question 230: Which of the fallowing statements is MOST accurate regarding...
- Question 231: When deploying en Intrusion Detection System (IDS) on a high...
- Question 232: Which of the following is the FIRST requirement a data owner...
- Question 233: Which of the following techniques is known to be effective i...
- Question 234: The Structured Query Language (SQL) implements Discretionary...
- Question 235: What requirement MUST be met during internal security audits...
- Question 236: A company wants to implement two-factor authentication (2FA)...
- Question 237: Which of the following BEST describes the purpose of "Egress...
- Question 238: Which of the following is a MAJOR concern when there is a ne...
- Question 239: Which type of test would an organization perform in order to...
- Question 240: A Security Operations Center (SOC) receives an incident resp...
- Question 241: The use of proximity card to gain access to a building is an...
- Question 242: Why would a security architect specify that a default route ...
- Question 243: An information security administrator wishes to block peer-t...
- Question 244: What is an advantage of Elliptic Curve Cryptography (ECC)?...
- Question 245: Which part of an operating system (OS) is responsible for pr...
- Question 246: A digitally-signed e-mail was delivered over a wireless netw...
- Question 247: Which of the following is a detective access control mechani...
- Question 248: The Chief Information Security Officer (CISO) of an organiza...
- Question 249: Who has the PRIMARY responsibility to ensure that security o...
- Question 250: How does Encapsulating Security Payload (ESP) in transport m...
- Question 251: What BEST describes the confidentiality, integrity, availabi...
- Question 252: Which of the following is ensured when hashing files during ...
- Question 253: A small office is running WiFi 4 APs, and neighboring office...
- Question 254: Which of the following practices provides the development te...
- Question 255: Which of the following is a PRIMARY challenge when running a...
- Question 256: Within a large organization, what business unit is BEST posi...
- Question 257: Building blocks for software-defined networks (SDN) require ...
- Question 258: Which of the following is considered a secure coding practic...
- Question 259: Which of the following entails identification of data and li...
- Question 260: Which of the following Disaster Recovery (DR) sites is the M...
- Question 261: An organization would like to ensure that all new users have...
- Question 262: An employee of a retail company has been granted an extended...
- Question 263: Which reporting type requires a service organization to desc...
- Question 264: Retaining system logs for six months or longer can be valuab...
- Question 265: Why is planning in Disaster Recovery (DR) an interactive pro...
- Question 266: Of the following, which BEST provides non- repudiation with ...
- Question 267: An organization is setting a security assessment scope with ...
- Question 268: Which of the following activities is MOST likely to be perfo...
- Question 269: Which of the following is the BEST mitigation from phishing ...
- Question 270: What is the FIRST step when developing an Information Securi...
- Question 271: Assessing a third party's risk by counting bugs in the code ...
- Question 272: Which of the following BEST describes the purpose of an "Egr...
- Question 273: Drag and Drop Question Given the various means to protect ph...
- Question 274: Which of the following is the BEST solution to provide redun...
- Question 275: An organization has outsourced its financial transaction pro...
- Question 276: A network administrator is configuring a database server and...
- Question 277: What is the PRIMARY consideration when testing industrial co...
- Question 278: Which of the following can BEST prevent security flaws occur...
- Question 279: Which one of the following is the MOST important in designin...
- Question 280: Which of the following is a key responsibility for a data st...
- Question 281: In a large company, a system administrator needs to assign u...
- Question 282: Which of the following is established to collect information...
- Question 283: A user's credential for an application is stored in a relati...
- Question 284: An organization recently upgraded to a Voice over Internet P...
- Question 285: In a change-controlled environment, which of the following i...
- Question 286: What is the BEST way to establish identity over the internet...
- Question 287: A security analyst for a large financial institution is revi...
- Question 288: What is the MOST significant benefit of an application upgra...
- Question 289: Which of the following is needed to securely distribute symm...
- Question 290: What do Capability Maturity Models (CMM) serve as a benchmar...
- Question 291: Which of the following routing protocols is used to exchange...
- Question 292: When reviewing vendor certifications for handling and proces...
- Question 293: An organization's risk management team calculates that a spe...
- Question 294: In setting expectations when reviewing the results of a secu...
- Question 295: A software architect has been asked to build a platform to d...
- Question 296: What are facets of trustworthy software in supply chain oper...
- Question 297: Which of the following BEST describes the purpose of "Egress...
- Question 298: Which of the following determines how traffic should flow ba...
- Question 299: A developer begins employment with an information technology...
- Question 300: Which of the following media sanitization techniques is MOST...
- Question 301: Which of the following poses the GREATEST privacy risk to pe...
- Question 302: A cloud service provider requires its customer organizations...
- Question 303: Which of the following is the PRIMARY risk with using open s...
- Question 304: Which of the following is the BEST way to protect an organiz...
- Question 305: What is the term commonly used to refer to a technique of au...
- Question 306: The birthday attack is MOST effective against which one of t...
- Question 307: Which of the following activities BEST identifies operationa...
- Question 308: Which of the following is a covert channel type?...
- Question 309: During testing, where are the requirements to inform parent ...
- Question 310: Which type of security testing is being performed when an et...
- Question 311: Which of the following is an appropriate source for test dat...
- Question 312: Which of the following departments initiates the request, ap...
- Question 313: Which of the following BEST describes the "clean desk policy...
- Question 314: An organization has decided to contract with a cloud-based s...
- Question 315: The Secure Shell (SSH) version 2 protocol supports....
- Question 316: Which of the following are the B EST characteristics of secu...
- Question 317: The PRIMARY purpose of accreditation is to:...
- Question 318: Regarding asset security and appropriate retention, which of...
- Question 319: Which security modes is MOST commonly used in a commercial e...
- Question 320: Which of the following will help identify the source interne...
- Question 321: Configuring a Wireless Access Point (WAP) with the same Serv...
- Question 322: Which of the following is the MOST beneficial to review when...
- Question 323: Changes to a Trusted Computing Base (TCB) system that could ...
- Question 324: During an audit, the auditor finds evidence of potentially i...
- Question 325: A cloud service accepts Security Assertion Markup Language (...
- Question 326: Which of the following is the BEST technique to facilitate s...
- Question 327: A health care provider is considering Internet access for th...
- Question 328: A system is developed so that its business users can perform...
- Question 329: Which of the following provides the MOST protection against ...
- Question 330: The FIRST step in building a firewall is to...
- Question 331: An international organization has decided to use a Software ...
- Question 332: Which of the following describes the BEST configuration mana...
- Question 333: Which cryptographic attack involves an attacker obtaining pa...
- Question 334: Which of the following is the PRIMARY goal of a Data Loss Pr...
- Question 335: An organization outgrew its internal data center and is eval...
- Question 336: In software development, which of the following entities nor...
- Question 337: An organization is preparing to achieve General Data Protect...
- Question 338: Which of the following is generally indicative of a replay a...
- Question 339: When a flaw in Industrial control (ICS) software is discover...
- Question 340: Which of the following is a process within a Systems Enginee...
- Question 341: Software Code signing is used as a method of verifying what ...
- Question 342: Which of the following would be the BEST mitigation practice...
- Question 343: Which of the following BEST describes "Immutable Infrastruct...
- Question 344: During an investigation of database theft from an organizati...
- Question 345: A security professional has been requested by the Board of D...
- Question 346: What is the MOST efficient way to secure a production progra...
- Question 347: Which of the following is the BEST defense against password ...
- Question 348: During the risk assessment phase of the project the CISO dis...
- Question 349: Which of the following is the MOST important consideration w...
- Question 350: Which of the following BEST describes the "Bell-LaPadula" se...
- Question 351: Which of the following security tools will ensure authorized...
- Question 352: The overall goal of a penetration test is to determine a sys...
- Question 353: A fiber link connecting two campus networks is broken. Which...
- Question 354: After a breach incident, investigators narrowed the attack t...
- Question 355: Which of the following are required components for implement...
- Question 356: Which of the following BEST describes the responsibilities o...
- Question 357: An organization has hired a security services firm to conduc...
- Question 358: Which of the following factors contributes to the weakness o...
- Question 359: A subscription service which provides power, climate control...
- Question 360: Which type of intrusion detection system (IDS) compares obse...
- Question 361: Which of the following management process allows ONLY those ...
- Question 362: What physical characteristic does a retinal scan biometric d...
- Question 363: Who is accountable for the information within an Information...
- Question 364: What is an effective practice when returning electronic stor...
- Question 365: What type of database attack would allow a customer service ...
- Question 366: Which of the following protocols is used to securely resolve...
- Question 367: What term is commonly used to describe hardware and software...
- Question 368: Which of the following BEST describes the purpose of "Egress...
- Question 369: The Industrial Control System (ICS) Computer Emergency Respo...
- Question 370: What are the steps of a risk assessment?...
- Question 371: For the purpose of classification, which of the following is...
- Question 372: Which of the following BEST describes the purpose of "Egress...
- Question 373: In supervisory control and data acquisition (SCADA) systems,...
- Question 374: What is the FIRST step in developing a patch management plan...
- Question 375: Which of the following is the MOST accurate description of "...
- Question 376: Which of the following BEST describes "Business Continuity P...
- Question 377: Directive controls are a form of change management policy an...
- Question 378: An Information Technology (IT) professional attends a cybers...
- Question 379: What is the process of removing sensitive data from a system...
- Question 380: Which of the following BEST describes the purpose of perform...
- Question 381: A company receives an email threat informing of an Imminent ...
- Question 382: Which of the following BEST describes the concept of "least ...
- Question 383: Which of the following is a remote access protocol that uses...
- Question 384: Which of the following management processes allots ONLY thos...
- Question 385: Which of the following BEST describes "Threat Hunting"?...
- Question 386: Which of the following is included in change management?...
- Question 387: Which of the following actions should be taken by a security...
- Question 388: Which is the RECOMMENDED configuration mode for sensors for ...
- Question 389: Which of the following is TRUE for an organization that is u...
- Question 390: A firm within the defense industry has been directed to comp...
- Question 391: Which of the following is MOST appropriate to collect eviden...
- Question 392: A proxy firewall operates at what layer of the Open System I...
- Question 393: Which of the following are mandatory canons for the (ISC)* C...
- Question 394: Which of the following BEST describes the responsibilities o...
- Question 395: An organization is designing a large enterprise-wide documen...
- Question 396: A security professional can BEST mitigate the risk of using ...
- Question 397: What is the BEST approach for controlling access to highly s...
- Question 398: A hospital has allowed virtual private networking (VPN) acce...
- Question 399: When assessing an organization's security policy according t...
- Question 400: Who should formulate conclusions from a particular digital f...
- Question 401: By allowing storage communications to run on top of Transmis...
- Question 402: Which of the following is a process in the access provisioni...
- Question 403: What is the purpose of an Internet Protocol (IP) spoofing at...
- Question 404: Which of the following BEST describes the "Star Property" (-...
- Question 405: An enterprise is developing a baseline cybersecurity standar...
- Question 406: When telephones in a city are connected by a single exchange...
- Question 407: Which of the following was developed to support multiple pro...
- Question 408: Which of the following is the BEST way to mitigate circumven...
- Question 409: A new Chief Information Officer (CIO) created a group to wri...
- Question 410: Which of the following BEST describes the purpose of "Securi...
- Question 411: An organization publishes and periodically updates its emplo...
- Question 412: When designing a Cyber-Physical System (CPS), which of the f...
- Question 413: The goal of a Business Continuity Plan (BCP) training and aw...
- Question 414: Which of the following BEST describes "Asymmetric" encryptio...
- Question 415: What type of wireless network attack BEST describes an Elect...
- Question 416: Which of the following is the BEST method to gather evidence...
- Question 417: Which of the following presents the PRIMARY concern to an or...
- Question 418: What is the PRIMARY purpose of auditing, as it relates to th...
- Question 419: Which of the following is an advantage of on premise Credent...
- Question 420: When developing solutions for mobile devices, in which phase...
- Question 421: Which of the following MOST applies to session initiation pr...
- Question 422: Which of the following BEST describes the purpose of Border ...
- Question 423: What is the BEST way to correlate large volumes of disparate...
- Question 424: Continuity of operations is BEST supported by which of the f...
- Question 425: Which of the following assures that rules are followed in an...
- Question 426: Which of the following is the MAIN reason for using configur...
- Question 427: While classifying credit card data related to Payment Card I...
- Question 428: What is the MOST important consideration from a data securit...
- Question 429: Which of the following BEST describes "Formal Methods" in se...
- Question 430: Even though a particular digital watermark is difficult to d...
- Question 431: Which of the following reports provides the BEST attestation...
- Question 432: Which of the following access control models grants or denie...
- Question 433: Which of the following BEST describes "Data Sovereignty" as ...
- Question 434: A large university needs to enable student access to univers...
- Question 435: An organization has requested storage area network (SAN) dis...
- Question 436: While reviewing the financial reporting risks of a third-par...
- Question 437: Which of the following BEST describes a chosen plaintext att...
- Question 438: Which of the following needs to be included in order for Hig...
- Question 439: Refer to the information below to answer the question. A sec...
- Question 440: Which one of the following is a common risk with network con...
- Question 441: Which of the following information MUST be provided for user...
- Question 442: When network management is outsourced to third parties, whic...
- Question 443: What is a characteristic of Secure Socket Layer (SSL) and Tr...
- Question 444: Which is the BEST control to meet the Statement on Standards...
- Question 445: A Chief Information Security Officer (CISO) of a firm which ...
- Question 446: Which of the following open source software issues pose the ...
- Question 447: Which of the following BEST obtains an objective audit of se...
- Question 448: Which of the following is a MUST for creating a new custom-b...
- Question 449: Which of the following attack types can be used to compromis...
- Question 450: At what stage of the Software Development Life Cycle (SDLC) ...
- Question 451: Which of the following BEST describes "Role-Based Access Con...
- Question 452: Which of the following is the reason that transposition ciph...
- Question 453: Which of the following VPN configurations should be used to ...
- Question 454: Hotspot Question Which Web Services Security (WS-Security) s...
- Question 455: A corporate security policy specifies that all devices on th...
- Question 456: Which of the following is the MOST important output from a m...
- Question 457: During a recent assessment an organization has discovered th...
- Question 458: Which of the following is TRUE about Disaster Recovery Plan ...
- Question 459: The security organization is looking for a solution that cou...
- Question 460: Which of the following BEST describes "Time-Based One-Time P...
- Question 461: When a system changes significantly, who is PRIMARILY respon...
- Question 462: What are the three key benefits that application developers ...
- Question 463: Which of the following BEST describes the purpose of "Chaos ...
- Question 464: Which of the following BEST describes a rogue Access Point (...
- Question 465: Which of the following is a limitation of the Bell-LaPadula ...
- Question 466: Which of the following BEST describes "Whaling" as a type of...
- Question 467: A software engineer uses automated tools to review applicati...
- Question 468: Which of the following BEST describes the purpose of "Securi...
- Question 469: Which of the following is the PRIMARY reason for employing p...
- Question 470: Which security architecture strategy could be applied to sec...
- Question 471: As a security manger which of the following is the MOST effe...
- Question 472: Which of the following BEST describes "Time-of-Check to Time...
- Question 473: Which of the following is the MOST effective countermeasure ...
- Question 474: What is the PRIMARY difference between security policies and...
- Question 475: What is the PRIMARY benefit of relying on Security Content A...
- Question 476: Which of the following is a correct feature of a virtual loc...
- Question 477: Refer to the information below to answer the question. A lar...
- Question 478: Which of the following is the MOST appropriate control for a...
- Question 479: An external attacker has compromised an organization's netwo...
- Question 480: When reviewing the security logs, the password shown for an ...
- Question 481: What protocol is often used between gateway hosts on the Int...
- Question 482: An information technology (IT) employee who travels frequent...
- Question 483: Which of the following BEST describes "Living-off-the-Cloud"...
- Question 484: Which of the following is the PRIMARY mechanism used to limi...
- Question 485: How is Remote Authentication Dial-In User Service (RADIUS) a...
- Question 486: What are the essential elements of a Risk Assessment Report ...
- Question 487: Which of the following BEST describes the purpose of "Egress...
- Question 488: Which of the following is a method of attacking internet (IP...
- Question 489: What is the MOST effective response to a hacker who has alre...
- Question 490: Which of the following roles has the obligation to ensure th...
- Question 491: Which of the following BEST describes "Business Continuity: ...
- Question 492: Which Wide Area Network (WAN) technology requires the first ...
- Question 493: Which of the following models uses unique groups contained i...
- Question 494: Without proper signal protection, embedded systems may be pr...
- Question 495: Which layer of the Open system Interconnect (OSI) model is r...
- Question 496: Which of the following methods of suppressing a fire is envi...
- Question 497: What is the GREATEST challenge of an agent-based patch manag...
- Question 498: The BEST method to mitigate the risk of a dictionary attack ...
- Question 499: Who is responsible for the protection of information when it...
- Question 500: Which of the following BEST describes "Continuous Integratio...
- Question 501: Which of the following types of firewall only examines the "...
- Question 502: Refer to the information below to answer the question. A lar...
- Question 503: Which of the following is the MOST effective strategy to pre...
- Question 504: A security practitioner is tasked with securing the organiza...
- Question 505: Which of the following BEST describes the purpose of "Egress...
- Question 506: During which of the following processes is least privilege i...
- Question 507: Which of the following determines how traffic should flow ba...
- Question 508: What is the PRIMARY role of a scrum master in agile developm...
- Question 509: Which of the following is an authentication protocol in whic...
- Question 510: Due to system constraints, a group of system administrators ...
- Question 511: Refer to the information below to answer the question. Deskt...
- Question 512: Which of the following techniques is effective to detect tap...
- Question 513: The acquisition of personal data being obtained by a lawful ...
- Question 514: When developing a business case for updating a security prog...
- Question 515: Which of the following is the BEST way to reduce the impact ...
- Question 516: Which of the following BEST describes "Business Continuity: ...
- Question 517: The principle that personally identifiable information (PII)...
- Question 518: What is the FIRST step required in establishing a records re...
- Question 519: Which Open Systems Interconnection (OSI) layer(s) BEST corre...
- Question 520: Drag and Drop Question Match the objectives to the assessmen...
- Question 521: Which of the following is the PRIMARY reason a sniffer opera...
- Question 522: Which of the below strategies would MOST comprehensively add...
- Question 523: What is the HIGHEST priority in agile development?...
- Question 524: In the common criteria (CC) for information technology (IT) ...
- Question 525: What would be the BEST action to take in a situation where c...
- Question 526: When using Generic Routing Encapsulation (GRE) tunneling ove...
- Question 527: Digital non-repudiation requires which of the following?...
- Question 528: Which of the following is the PRIMARY purpose of due diligen...
- Question 529: How can a security engineer maintain network separation from...
- Question 530: Application of which of the following Institute of Electrica...
- Question 531: Who in the organization is accountable for classification of...
- Question 532: Which of the following BEST describes the purpose of "Egress...
- Question 533: During examination of Internet history records, the followin...
- Question 534: Which of the following is MOST important to follow when deve...
- Question 535: Which of the following is required to determine classificati...
- Question 536: Before allowing a web application into the production enviro...
- Question 537: Information security practitioners are in the midst of imple...
- Question 538: Which of the following BEST describes the purpose of "Egress...
- Question 539: Which of the following is the MOST effective measure for dea...
- Question 540: Drag and Drop Question Place in order, from BEST (1) to WORS...
- Question 541: Which of the following BEST describes "Egress Point Behavior...
- Question 542: Which software defined networking (SDN) architectural compon...
- Question 543: How does security in a distributed file system using mutual ...
- Question 544: Which of the following BEST describes the purpose of "Egress...
- Question 545: Refer to the information below to answer the question. A lar...
- Question 546: A company-wide penetration test result shows customers could...
- Question 547: Which of the following BEST describes the purpose of "Egress...
- Question 548: In order to assure authenticity, which of the following are ...
- Question 549: The BEST method of demonstrating a company's security level ...
- Question 550: A hospital has three data classification levels: shareable w...
- Question 551: What security management control is MOST often broken by col...
- Question 552: Which of the following is the MOST important security goal w...
- Question 553: Which of the following is an important requirement when desi...
- Question 554: A company hired an external vendor to perform a penetration ...
- Question 555: Which of the following MUST be done before a digital forensi...
- Question 556: Which of the following frameworks provides vulnerability met...
- Question 557: What component of a web application that stores the session ...
- Question 558: In an IDEAL encryption system, who has sole access to the de...
- Question 559: Drag and Drop Question Match the level of evaluation to the ...
- Question 560: An organization is trying to secure instant messaging (IM) c...
- Question 561: As part of the security assessment plan, the security profes...
- Question 562: Why is planning the MOST critical phase of a Role Based Acce...
- Question 563: Which of the following BEST describes the concept of "chain ...
- Question 564: Which area of embedded devices are most commonly attacked?...
- Question 565: An Internet media company produces and broadcasts highly pop...
- Question 566: Which of the following BEST describes the purpose of "Egress...
- Question 567: A security architect plans to reference a Mandatory Access C...
- Question 568: Which of the following BEST describes the purpose of softwar...
- Question 569: When designing a networked Information System (IS) where the...
- Question 570: Which of the following is the BIGGEST weakness when using na...
- Question 571: An organization plan on purchasing a custom software product...
- Question 572: A security practitioner has been asked to model best practic...
- Question 573: Which of the following is part of a Trusted Platform Module ...
- Question 574: An organization has developed a way for customers to share i...
- Question 575: Spyware is BEST described as
- Question 576: An international trading organization that holds an Internat...
- Question 577: Which of the following is a canon of the (ISC)2 Code of Ethi...
- Question 578: After acquiring the latest security updates, what must be do...
- Question 579: Which of the following BEST describes the purpose of "Egress...
- Question 580: Which of the following is a unique feature of attribute-base...
- Question 581: When in the Software Development Life Cycle (SDLC) MUST soft...
- Question 582: A mobile device application that restricts the storage of us...
- Question 583: Which type of disaster recovery plan (DRP) testing carries t...
- Question 584: A criminal organization is planning an attack on a governmen...
- Question 585: Which of the following BEST describes "Post-Quantum Cryptogr...
- Question 586: The use of private and public encryption keys is fundamental...
- Question 587: A bank failed to meet service-level agreements (SLA) with cu...
- Question 588: Which of the following mobile code security models relies on...
- Question 589: Which of the following protects personally identifiable info...
- Question 590: Drag and Drop Question A software security engineer is devel...
- Question 591: What is the threat modeling order using process for Attack s...
- Question 592: Which of the following System and Organization Controls (SOC...
- Question 593: Which of the following is a peor entity authentication metho...
- Question 594: Which of the following is the BEST description of "Software ...
- Question 595: Which of the following BEST describes the purpose of a "Base...
- Question 596: Which of the following is the BEST approach to take in order...
- Question 597: What type of investigation applies when malicious behavior i...
- Question 598: In an organization where Network Access Control (NAC) has be...
- Question 599: Which of the following BEST describes "Confidential Computin...
- Question 600: An Intrusion Detection System (IDS) is generating alarms tha...
- Question 601: Which of the following BEST describes "Egress Point Adaptive...
- Question 602: An advantage of link encryption in a communications network ...
- Question 603: When transmitting information over public networks, the deci...
- Question 604: Internet Protocol (IP) source address spoofing is used to de...
- Question 605: Which is the PRIMARY mechanism for providing the workforce w...
- Question 606: Which of the following BEST describes the purpose of "Egress...
- Question 607: Why do certificate Authorities (CA) add value to the securit...
- Question 608: Which of the following BEST describes the purpose of a "Post...
- Question 609: Which of the following terms is used for online service prov...
- Question 610: Which of the following BEST describes the purpose of "Egress...
- Question 611: Which of the following techniques evaluates the secure Bet p...
- Question 612: A database administrator is asked by a high-ranking member o...
- Question 613: Which of the following actions will reduce risk to a laptop ...
- Question 614: A colleague who recently left the organization asked a secur...
- Question 615: Which of the following is the PRIMARY consideration when det...
- Question 616: Which of the following BEST describes the concept of "Non-Re...
- Question 617: A technician is troubleshooting a client's report about poor...
- Question 618: Following the completion of a network security assessment, w...
- Question 619: Which of the following objects should be removed FIRST prior...
- Question 620: The goal of a Business Impact Analysis (BIA) is to determine...
- Question 621: What is an important characteristic of Role Based Access Con...
- Question 622: What is the BEST way to restrict access to a file system on ...
- Question 623: Which of the following BEST describes the purpose of "Egress...
- Question 624: How is it possible to extract private keys securely stored o...
- Question 625: Which of the following BEST describes "Cold Site" disaster r...
- Question 626: Which of the following BEST describes "Availability" as one ...
- Question 627: Which of the following wraps the decryption key of a full di...
- Question 628: Which of the following is the GREATEST benefit of implementi...
- Question 629: Although code using a specific program language may not be s...
- Question 630: Which of the following BEST mitigates a replay attack agains...
- Question 631: Which of the following types of datacenter architectures wil...
- Question 632: Which of the following BEST describes the purpose of "Egress...
- Question 633: Why is a system's criticality classification important in la...
- Question 634: Which of the following MUST be scalable to address security ...
- Question 635: In the Software Development Life Cycle (SDLC), maintaining a...
- Question 636: From an asset security perspective, what is the BEST counter...
- Question 637: An organization is considering partnering with a third-party...
- Question 638: Which of the following BEST describes the purpose of "Egress...
- Question 639: Which of the following prevents improper aggregation of priv...
- Question 640: What high Availability (HA) option of database allows multip...
- Question 641: Which of the following is the BEST way to determine if a par...
- Question 642: A large organization's human resources and security teams ar...
- Question 643: The security architect has been assigned the responsibility ...
- Question 644: Which of the following encryption technologies has the abili...
- Question 645: Which of the following types of hosts should be operating in...
- Question 646: Which of the following analyses is performed to protect info...
- Question 647: The MAIN use of Layer 2 Tunneling Protocol (L2TP) is to tunn...
- Question 648: During a Disaster Recovery (DR) assessment, additional cover...
- Question 649: Which of the following BEST describes when an organization s...
- Question 650: Which application type is considered high risk and provides ...
- Question 651: An organization is planning to have an it audit of its as a ...
- Question 652: A security practitioner detects an Endpoint attack on the or...
- Question 653: What is the PRIMARY benefit of incident reporting and comput...
- Question 654: What would be the MOST cost effective solution for a Disaste...
- Question 655: An internal Service Level Agreement (SLA) covering security ...
- Question 656: A large corporation is looking for a solution to automate ac...
- Question 657: What industry-recognized document could be used as a baselin...
- Question 658: Which of the following BEST describes "Two-Person Integrity"...
- Question 659: What is the PRIMARY purpose of creating and reporting metric...
- Question 660: An organization is implementing security review as part of s...
- Question 661: What is the FIRST step in developing a security test and its...
- Question 662: In Federated Identity Management (FIM), which of the followi...
- Question 663: What type of access control determines the authorization to ...
- Question 664: A company is enrolled in a hard drive reuse program where de...
- Question 665: In organization discovers that its secure file transfer prot...
- Question 666: Which of the following BEST describes the purpose of "Tablet...
- Question 667: Which of the following virtual network configuration options...
- Question 668: Which of the following BEST describes "Model Poisoning" as a...
- Question 669: Additional padding may be added to toe Encapsulating Securit...
- Question 670: Drag and Drop Question Match the functional roles in an exte...
- Question 671: An organization is looking to improve threat detection on th...
- Question 672: An organization allows ping traffic into and out of their ne...
- Question 673: The type of authorized interactions a subject can have with ...
- Question 674: When network management is outsourced to third parties, whic...
- Question 675: A security professional determines that a number of outsourc...
- Question 676: What is the BEST location in a network to place Virtual Priv...
- Question 677: An employee receives a promotion that entities them to acces...
- Question 678: Which of the following is a common risk with fiber optical c...
- Question 679: Which of the following BEST describes "Elliptic Curve Crypto...
- Question 680: Which of the following is the BEST reason for the use of sec...
- Question 681: In order for application developers to detect potential vuln...
- Question 682: Which is the FIRST action the Incident Response team should ...
- Question 683: Which of the following BEST describes "Watering Hole" attack...
- Question 684: As a best practice, the Security Assessment Report (SAR) sho...
- Question 685: When would an organization review a Business Continuity Mana...
- Question 686: A cloud hosting provider would like to provide a Service Org...
- Question 687: What is the BEST approach to anonymizing personally identifi...
- Question 688: Which of the following steps is performed during the forensi...
- Question 689: Drag and Drop Question Place the following information class...
- Question 690: An organization requires that backup media be stored at a lo...
- Question 691: Which of the following BEST describes "Security Through Obsc...
- Question 692: Which of the following could cause a Denial of Service (DoS)...
- Question 693: Which of the following is the BEST method to reduce the effe...
- Question 694: Which of the following is the weakest form of protection for...
- Question 695: Which of the following is the FIRST step for defining Servic...
- Question 696: Which of the following BEST describes "tokenization" as a da...
- Question 697: An organization is attempting to strengthen the configuratio...
- Question 698: Which of the following is the BEST statement for a professio...
- Question 699: What is the process called when impact values are assigned t...
- Question 700: Compared to a traditional network, which of the following is...
- Question 701: With what frequency should monitoring of a control occur whe...
- Question 702: Checking routing information on e-mail to determine it is in...
- Question 703: During the Security Assessment and Authorization process, wh...
- Question 704: Which of the following could elicit a Denial of Service (DoS...
- Question 705: A retail company is looking to start a development project t...
- Question 706: Hotspot Question Which Web Services Security (WS-Security) s...
- Question 707: Company A is evaluating new software to replace an in-house ...
- Question 708: Recently, an unknown event has disrupted a single Layer-2 ne...
- Question 709: Which of the following BEST describes "input validation" as ...
- Question 710: An organization wants to enable uses to authenticate across ...
- Question 711: What is the BEST reason to include supply chain risks in a c...
- Question 712: Which type of fire alarm system sensor is intended to detect...
- Question 713: When configuring Extensible Authentication Protocol (EAP) in...
- Question 714: Why are mobile devices something difficult to investigate in...
- Question 715: A company seizes a mobile device suspected of being used in ...
- Question 716: What form of attack could this represent?...
- Question 717: What is the PRIMARY goal for using Domain Name System Securi...
- Question 718: The PRIMARY security concern for handheld devices is the...
- Question 719: An organization is required to comply with the Payment Card ...
- Question 720: Which of the following BEST describes "shoulder surfing"?...
- Question 721: When assessing the audit capability of an application, which...
- Question 722: Which of the following criteria ensures information is prote...
- Question 723: Which of the following methods is MOST effective in mitigati...
- Question 724: In general, servers that are facing the Internet should be p...
- Question 725: Organization A is adding a large collection of confidential ...
- Question 726: Refer to the information below to answer the question. A lar...
- Question 727: Which of the following is a physical security control that p...
- Question 728: Which section of the assessment report addresses separate vu...
- Question 729: Refer to the information below to answer the question. A new...
- Question 730: When using third-party software developers, which of the fol...
- Question 731: What method could be used to prevent passive attacks against...
- Question 732: Which of the following attacks is dependent upon the comprom...
- Question 733: Which of the following is an open standard for exchanging au...
- Question 734: What is the purpose of code signing?...
- Question 735: Which of the following is the MAIN goal of a data retention ...
- Question 736: An engineer notices some late collisions on a half-duplex li...
- Question 737: What is the PRIMARY objective of business continuity plannin...
- Question 738: How should the retention period for an organization's social...
- Question 739: Which of the following secures web transactions at the Trans...
- Question 740: Which of the BEST internationally recognized standard for ev...
- Question 741: Which of the following MUST a security professional do in or...
- Question 742: Which of the following has the GREATEST impact on an organiz...
- Question 743: What is the expected outcome of security awareness in suppor...
- Question 744: What is the PRIMARY reason criminal law is difficult to enfo...
- Question 745: Which of the following BEST describes "Cyber Kill Chain" as ...
- Question 746: Which of the following BEST describes "Shadow IT"?...
- Question 747: Refer to the information below to answer the question. An or...
