- Home
- Curam Software
- CompTIA Cybersecurity Analyst (CySA+) Certification Exam
- CuramSoftware.CS0-003.v2026-09-21.q313
- Question 286
Valid CS0-003 Dumps shared by ExamDiscuss.com for Helping Passing CS0-003 Exam! ExamDiscuss.com now offer the newest CS0-003 exam dumps, the ExamDiscuss.com CS0-003 exam questions have been updated and answers have been corrected get the newest ExamDiscuss.com CS0-003 dumps with Test Engine here:
Access CS0-003 Dumps Premium Version
(517 Q&As Dumps, 35%OFF Special Discount Code: freecram)
<< Prev Question Next Question >>
Question 286/313
SIMULATION
A company recently experienced a security incident. The security team has determined a user clicked on a link embedded in a phishing email that was sent to the entire company. The link resulted in a malware download, which was subsequently installed and run.
INSTRUCTIONS
Part 1
Review the artifacts associated with the security Incident. Identify the name of the malware, the malicious IP address, and the date and time when the malware executable entered the organization.
Part 2
Review the kill chain items and select an appropriate control for each that would improve the security posture of the organization and would have helped to prevent this incident from occurring. Each control may only be used once, and not all controls will be used.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
Firewall log:


File integrity Monitoring Report:


Malware domain list:

Vulnerability Scan Report:


Phishing Email:


A company recently experienced a security incident. The security team has determined a user clicked on a link embedded in a phishing email that was sent to the entire company. The link resulted in a malware download, which was subsequently installed and run.
INSTRUCTIONS
Part 1
Review the artifacts associated with the security Incident. Identify the name of the malware, the malicious IP address, and the date and time when the malware executable entered the organization.
Part 2
Review the kill chain items and select an appropriate control for each that would improve the security posture of the organization and would have helped to prevent this incident from occurring. Each control may only be used once, and not all controls will be used.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
Firewall log:
File integrity Monitoring Report:
Malware domain list:
Vulnerability Scan Report:
Phishing Email:
Correct Answer:
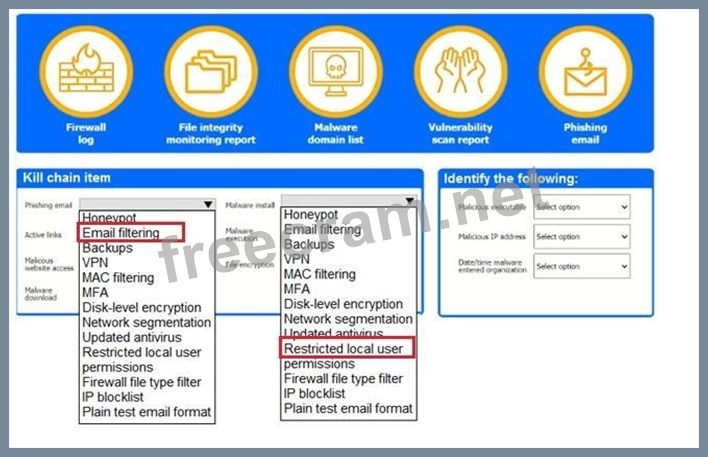
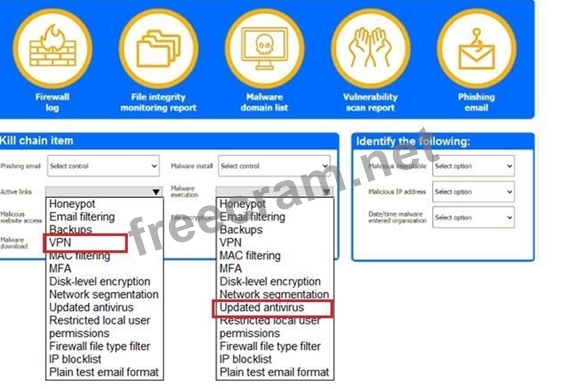
Kill Chain Item:
Phishing email - Email filtering
Active links - VPN
Malicious website access - IP blocklist
Malware download - Firewall file type filter
Malware install - Restricted local user permissions
Malware execution - Updated antivirus
File encryption - Backups
Identify the following:
Malicious executable - Payroll.xlsx
Malicious IP Address - 81.161.63.103
Date/time malware entered organization- 1 Dec 2019 14:03:19


- Question List (313q)
- Question 1: Which of the following is best suited for determining the me...
- Question 2: A small company does not have enough staff to effectively se...
- Question 3: An analyst is evaluating a vulnerability management dashboar...
- Question 4: Which of the following choices is most likely to cause obsta...
- Question 5: A security analyst is investigating a reported phishing atte...
- Question 6: An e-commerce organization recently experienced a cyberattac...
- Question 7: Which of the following best explains the importance of commu...
- Question 8: A security analyst is trying to validate the results of a we...
- Question 9: Which of the following should a cybersecurity analyst utiliz...
- Question 10: A security analyst has found the following suspicious DNS tr...
- Question 11: A security analyst needs to support an organization's legal ...
- Question 12: An organization wants to ensure the privacy of the data that...
- Question 13: A vulnerability analyst is writing a report documenting the ...
- Question 14: Which of the following is an important aspect that should be...
- Question 15: A security analyst responds to an incident and finds the att...
- Question 16: A developer downloaded and attempted to install a file trans...
- Question 17: The DevSecOps team is remediating an SSRF issue on the compa...
- Question 18: Which of the following best describes the action a technical...
- Question 19: A security manager reviews the permissions for the approved ...
- Question 20: A managed service provider manages servers in customer-assig...
- Question 21: Which of the following is the practice of controlling how ev...
- Question 22: A security analyst reviews the following results of a Nikto ...
- Question 23: After detecting possible malicious external scanning, an int...
- Question 24: Which of the following is a circumstance in which a security...
- Question 25: A cybersecurity analyst has recovered a recently compromised...
- Question 26: Which of the following best explains the importance of utili...
- Question 27: A vulnerability scanner has identified an out-of-support dat...
- Question 28: A company is in the process of implementing a vulnerability ...
- Question 29: A company's domain has been spooled in numerous phishing cam...
- Question 30: During a review of recent network traffic, an analyst realiz...
- Question 31: An organization performs software assurance activities and r...
- Question 32: An analyst is reviewing a vulnerability report for a server ...
- Question 33: During routine monitoring a security analyst identified the ...
- Question 34: After a recent vulnerability report for a server is presente...
- Question 35: After a security assessment was done by a third-party consul...
- Question 36: A security analyst observed the following activities in chro...
- Question 37: A security alert was triggered when an end user tried to acc...
- Question 38: A security analyst is reviewing events that occurred during ...
- Question 39: A security analyst found the following vulnerability on the ...
- Question 40: A company classifies security groups by risk level. Any grou...
- Question 41: When vulnerabilities are identified weeks after the disclosu...
- Question 42: An analyst is suddenly unable to enrich data from the firewa...
- Question 43: An analyst is reviewing system logs while threat hunting: (E...
- Question 44: A Chief Executive Officer (CEO) is concerned the company wil...
- Question 45: A security administrator has found indications of dictionary...
- Question 46: An analyst reviews the following list of vulnerabilities: (E...
- Question 47: A security analyst discovers an ongoing ransomware attack wh...
- Question 48: Which of the following best describes the reporting metric t...
- Question 49: A security analyst receives an alert with the following pack...
- Question 50: A user reports a message as suspicious to the IT security te...
- Question 51: There are several reports of sensitive information being dis...
- Question 52: An incident response team member is triaging a Linux server....
- Question 53: A security analyst needs to secure digital evidence related ...
- Question 54: Which of the following is an example of the shift-left conce...
- Question 55: A security analyst needs to identify an asset that should be...
- Question 56: Before adopting a disaster recovery plan, some team members ...
- Question 57: SIMULATION A healthcare organization must develop an action ...
- Question 58: Which of the following best describes the document that defi...
- Question 59: A security analyst found an old version of OpenSSH running o...
- Question 60: A security officer needs to find the most cost-effective sol...
- Question 61: A user's computer is performing slower than the day before, ...
- Question 62: A systems administrator reviews a ticket from a third-party ...
- Question 63: A group of hacktivists has breached and exfiltrated data fro...
- Question 64: A company patches its servers using automation software. Rem...
- Question 65: A security analyst at a company is reviewing an alert from t...
- Question 66: Which of the following explains how MTTD can affect IR repor...
- Question 67: Which of the following types of controls defines placing an ...
- Question 68: A security analyst reviews the following output: (Exhibit) W...
- Question 69: An analyst receives an alert for suspicious IIS log activity...
- Question 70: A penetration tester is conducting a test on an organization...
- Question 71: An end user forwarded an email with a file attachment to the...
- Question 72: During an incident, a security analyst discovers a large amo...
- Question 73: An organization utilizes multiple vendors, each with its own...
- Question 74: A security analyst detected the following suspicious activit...
- Question 75: A security analyst recently used Arachni to perform a vulner...
- Question 76: As part of a malware analysis, a security analyst finds the ...
- Question 77: A SOC manager is looking for a solution that can improve the...
- Question 78: Several critical bugs were identified during a vulnerability...
- Question 79: SIMULATION Approximately 100 employees at your company have ...
- Question 80: While conducting a cloud assessment, a security analyst perf...
- Question 81: During a security test, a security analyst found a critical ...
- Question 82: A BIA document was recently updated to include new critical ...
- Question 83: Which of the following would help to minimize human engageme...
- Question 84: Which of the following entities should an incident manager w...
- Question 85: A security analyst receives an alert for suspicious activity...
- Question 86: Which of the following describes a contract that is used to ...
- Question 87: A threat intelligence analyst is updating a document accordi...
- Question 88: Which of the following security operations tasks are ideal f...
- Question 89: An incident response team finished responding to a significa...
- Question 90: A security analyst notices multiple attempts of the same exp...
- Question 91: A vulnerability management team is unable to patch all vulne...
- Question 92: A security administrator is tasked with modifying the vulner...
- Question 93: A Chief Information Security Officer (CISO) has determined t...
- Question 94: An organization is preparing for a disaster recovery exercis...
- Question 95: An analyst is designing a message system for a bank. The ana...
- Question 96: During a recent site survey. an analyst discovered a rogue w...
- Question 97: Numerous emails were sent to a company's customer distributi...
- Question 98: A DevOps analyst must include code scanning in the current C...
- Question 99: A company has a primary control in place to restrict access ...
- Question 100: A company's user accounts have been compromised. Users are a...
- Question 101: Joe, a leading sales person at an organization, has announce...
- Question 102: An organization's internal department frequently uses a clou...
- Question 103: Which of the following actions would an analyst most likely ...
- Question 104: An analyst finds that duplicate entries may exist in the ass...
- Question 105: Executives at an organization email sensitive financial info...
- Question 106: An analyst is conducting routine vulnerability assessments o...
- Question 107: An organization's Chief Information Security Officer (CISO) ...
- Question 108: Which of the following is the main concept behind the use of...
- Question 109: The Chief Information Security Officer wants the same level ...
- Question 110: A company brings in a consultant to make improvements to its...
- Question 111: A security manager has decided to form a special group of an...
- Question 112: An organization has the following risk mitigation policies: ...
- Question 113: The majority of a company's employees have stated they are u...
- Question 114: The architecture team has been given a mandate to reduce the...
- Question 115: An organization has the following policy statements: - AlI e...
- Question 116: A security operations (SOC) manager develops response mechan...
- Question 117: Which of the following can a software provider use to implem...
- Question 118: During an extended holiday break, a company suffered a secur...
- Question 119: A junior security analyst opened ports on the company's fire...
- Question 120: While performing a dynamic analysis of a malicious file, a s...
- Question 121: An analyst is reviewing the following output as part of an i...
- Question 122: A company is deploying new vulnerability scanning software t...
- Question 123: Which of the following is a KPI that is used to monitor or r...
- Question 124: A security analyst is trying to identify anomalies on the ne...
- Question 125: A Chief Information Security Officer (CISO) has decided the ...
- Question 126: Which of the following threat-modeling procedures is in the ...
- Question 127: A security analyst detects an email server that had been com...
- Question 128: Hotspot Question A healthcare organization must develop an a...
- Question 129: An incident response team detected malicious software that c...
- Question 130: A SOC has SIEM configured to receive threat intelligence fee...
- Question 131: A Chief Information Security Officer has requested a dashboa...
- Question 132: A web application has a function to retrieve content from an...
- Question 133: A company has alerted planning the implemented a vulnerabili...
- Question 134: A threat hurting team received a new loC from an ISAC that f...
- Question 135: A security analyst is deploying a new application in the env...
- Question 136: An analyst is imaging a hard drive that was obtained from th...
- Question 137: An analyst is remediating items associated with a recent inc...
- Question 138: An analyst is reviewing a dashboard from the company's SIEM ...
- Question 139: The management team requests monthly KPI reports on the comp...
- Question 140: A cybersecurity analyst is doing triage in a SIEM and notice...
- Question 141: A company migrated its email solution from hybrid to on prem...
- Question 142: A security analyst identifies a device on which different ma...
- Question 143: A newly hired security manager in a SOC wants to improve eff...
- Question 144: Which of the following is the best framework for assessing h...
- Question 145: Which of the following best describes the importance of impl...
- Question 146: Security analysts can review the Windows Registry on endpoin...
- Question 147: Which of the following is the best option for an IT administ...
- Question 148: Which of the following is a reason why a SOC team member mig...
- Question 149: A security analyst has identified outgoing network traffic l...
- Question 150: A security analyst is reviewing a firewall usage report that...
- Question 151: Which of the following best describe the external requiremen...
- Question 152: Forming a hypothesis, looking for indicators of compromise, ...
- Question 153: Which of the following will most likely ensure that mission-...
- Question 154: A security analyst needs to develop a solution to protect a ...
- Question 155: An analyst would like to start automatically ingesting IoCs ...
- Question 156: An analyst uses an AI platform to help correlate events. The...
- Question 157: SIMULATION An organization has noticed large amounts of data...
- Question 158: A cybersecurity analyst is tasked with scanning a web applic...
- Question 159: Which of the following risk management decisions should be c...
- Question 160: A cybersecurity analyst needs to harden a server that is cur...
- Question 161: A threat intelligence analyst needs to gather TTPs from atta...
- Question 162: A company is in the middle of an incident, and customer data...
- Question 163: Which of the following attributes is part of the Diamond Mod...
- Question 164: While a security analyst for an organization was reviewing l...
- Question 165: A security analyst needs to provide evidence of regular vuln...
- Question 166: A software developer has been deploying web applications wit...
- Question 167: Which of the following is the most appropriate action a secu...
- Question 168: An analyst notices there is an internal device sending HTTPS...
- Question 169: An organization's email account was compromised by a bad act...
- Question 170: A security team is concerned about recent Layer 4 DDoS attac...
- Question 171: A company's application development has been outsourced to a...
- Question 172: A security analyst received an alert regarding multiple succ...
- Question 173: Which of the following security controls should be classifie...
- Question 174: An analyst finds that an IP address outside of the company n...
- Question 175: Each time a vulnerability assessment team shares the regular...
- Question 176: The Chief Information Security Officer (CISO) of a large fin...
- Question 177: An analyst reviews code for a sensitive application for thei...
- Question 178: Law enforcement subpoenas a company in order to obtain all r...
- Question 179: A company discovers that its proprietary information is bein...
- Question 180: A security analyst is reviewing the logs of a web server and...
- Question 181: A security analyst runs tcpdump on the 10.203.10.22 machine ...
- Question 182: During a cybersecurity incident, one of the web servers at t...
- Question 183: A security analyst is writing a shell script to identify IP ...
- Question 184: An analyst is reviewing a vulnerability report and must make...
- Question 185: A cryptocurrency service company is primarily concerned with...
- Question 186: A security analyst needs to identify a computer based on the...
- Question 187: During the rollout of a patch to the production environment,...
- Question 188: A security analyst working for an airline is prioritizing vu...
- Question 189: An older CVE with a vulnerability score of 7.1 was elevated ...
- Question 190: An analyst reviews a recent government alert on new zero-day...
- Question 191: A security analyst identifies the following log entry in the...
- Question 192: A company's internet-facing web application has been comprom...
- Question 193: During an incident, analysts need to rapidly investigate by ...
- Question 194: A WAF weekly report shows that a daily spike occurs from the...
- Question 195: An employee received a phishing email that contained malware...
- Question 196: Which of the following best describes the goal of a tabletop...
- Question 197: Several vulnerability scan reports have indicated runtime er...
- Question 198: Which of the following is a reason the false-positive rate i...
- Question 199: Which of the following explains why a company might repriori...
- Question 200: Which of the following would a security analyst most likely ...
- Question 201: An employee is no longer able to log in to an account after ...
- Question 202: An organization enabled a SIEM rule to send an alert to a se...
- Question 203: A security analyst discovers that, over three months, an att...
- Question 204: A Chief Finance Officer receives an email from someone who i...
- Question 205: An analyst wants to detect outdated software packages on a s...
- Question 206: A security analyst runs the following command: (Exhibit) Whi...
- Question 207: Which of the following most accurately describes the Cyber K...
- Question 208: Which of the following is a benefit of the Diamond Model of ...
- Question 209: A security analyst is conducting a vulnerability assessment ...
- Question 210: During a security incident at a healthcare facility, an unau...
- Question 211: Which of the following documents sets requirements and metri...
- Question 212: The Chief Information Security Officer for an organization r...
- Question 213: A high volume of failed RDP authentication attempts was logg...
- Question 214: Given the following report: (Exhibit) Which of the following...
- Question 215: An analyst recommends that an EDR agent collect the source I...
- Question 216: While reviewing web server logs, a security analyst discover...
- Question 217: The architecture team has been given a mandate to reduce the...
- Question 218: An analyst receives threat intelligence regarding potential ...
- Question 219: A systems administrator is concerned after reviewing the res...
- Question 220: A security analyst receives an alert with the following pack...
- Question 221: Which of the following statements best describes the MITRE A...
- Question 222: An analyst is evaluating the following vulnerability report:...
- Question 223: A security analyst is scanning an ICS host (192.168.1.5) in ...
- Question 224: The SOC receives a number of complaints regarding a recent u...
- Question 225: A SOC receives several alerts indicating user accounts are c...
- Question 226: Based on recent alerts, a security analyst thinks a web appl...
- Question 227: As part of an incident investigation, an analyst creates a d...
- Question 228: A security analyst has prepared a vulnerability scan that co...
- Question 229: An analyst is trying to capture anomalous traffic from a com...
- Question 230: Which of the following BEST explains the function of a manag...
- Question 231: A company is concerned with finding sensitive file storage l...
- Question 232: The security operations team is required to consolidate seve...
- Question 233: A company uses an FTP server to support its critical busines...
- Question 234: Which of the following is the term for a predefined set of a...
- Question 235: A Chief Information Security Officer wants to map all of the...
- Question 236: A manufacturing company's assembly line machinery only funct...
- Question 237: A recent audit of the vulnerability management program outli...
- Question 238: A security analyst responds to an alert regarding identity a...
- Question 239: A systems administrator needs to grant access to corporate s...
- Question 240: SIMULATION Welcome to the Enterprise Help Desk System. Pleas...
- Question 241: An incident response manager conducts a tabletop exercise. W...
- Question 242: A regulated organization experienced a security breach that ...
- Question 243: An organization has activated the CSIRT. A security analyst ...
- Question 244: Which of the following BEST describes what an organizations ...
- Question 245: A company has the following security requirements: - No publ...
- Question 246: A security analyst is trying to detect connections to a susp...
- Question 247: A red team engineer discovers that analyzing multiple pieces...
- Question 248: An IDS is triggered during after-hours operations. The indic...
- Question 249: A security analyst is assisting a software engineer with the...
- Question 250: Following an incident, a security analyst needs to create a ...
- Question 251: An employee is suspected of misusing a company-issued laptop...
- Question 252: A user is suspected of violating policy by logging in to a L...
- Question 253: Which of the following best explains compensating controls?...
- Question 254: The security team at a company, which was a recent target of...
- Question 255: A list of loCs released by a government security organizatio...
- Question 256: Which of the following ensures that a team receives simulate...
- Question 257: An organization would like to ensure its cloud infrastructur...
- Question 258: A security analyst needs to mitigate a known, exploited vuln...
- Question 259: An analyst is responding to an incident involving an attack ...
- Question 260: A security analyst discovers several vulnerabilities on a cr...
- Question 261: A security analyst reviews the following results of a Nikto ...
- Question 262: A company is implementing a vulnerability management program...
- Question 263: A security team conducts a lessons-learned meeting after str...
- Question 264: A security manager is looking at a third-party vulnerability...
- Question 265: Given the following CVSS string: CVSS:3.0/AV:N/AC:L/PR:N/UI:...
- Question 266: SIMULATION You are a cybersecurity analyst tasked with inter...
- Question 267: Which of the following describes the best reason for conduct...
- Question 268: A Chief Information Security Officer wants to lock down the ...
- Question 269: A systems administrator is reviewing after-hours traffic flo...
- Question 270: Which of the following is MOST dangerous to the client envir...
- Question 271: A security analyst needs to prioritize vulnerabilities for p...
- Question 272: A finance department employee opens an unsolicited email tha...
- Question 273: A user clicks on a malicious adware link, and the malware su...
- Question 274: To comply with regulatory requirements, the Chief Executive ...
- Question 275: A security analyst recently joined the team and is trying to...
- Question 276: K company has recently experienced a security breach via a p...
- Question 277: Which of the following is the best way to provide realistic ...
- Question 278: Which of the following techniques can help a SOC team to red...
- Question 279: A security analyst is analyzing two vulnerabilities on a cri...
- Question 280: An analyst has been asked to validate the potential risk of ...
- Question 281: A security analyst is improving an organization's vulnerabil...
- Question 282: While reviewing web server logs, an analyst notices several ...
- Question 283: A security analyst investigates a malware alert from a criti...
- Question 284: During an incident, an analyst needs to acquire evidence for...
- Question 285: A user is flagged for consistently consuming a high volume o...
- Question 286: SIMULATION A company recently experienced a security inciden...
- Question 287: A web developer reports the following error that appeared on...
- Question 288: While reviewing the web server logs a security analyst notic...
- Question 289: A company is launching a new application in its internal net...
- Question 290: A security analyst must review a suspicious email to determi...
- Question 291: A SOC manager is establishing a reporting process to manage ...
- Question 292: An analyst receives the following summary report for vulnera...
- Question 293: When investigating a potentially compromised host, an analys...
- Question 294: A security analyst scans a host and generates the following ...
- Question 295: A new cybersecurity analyst is tasked with creating an execu...
- Question 296: A security analyst is developing a script to filter firewall...
- Question 297: A security analyst wants to implement new monitoring control...
- Question 298: A company received a shipment of new network switches. Immed...
- Question 299: A leader on the vulnerability management team is trying to r...
- Question 300: A security analyst is implementing a process to perform vuln...
- Question 301: An organization conducted a web application vulnerability as...
- Question 302: A network security analyst for a large company noticed unusu...
- Question 303: A SOC manager receives a phone call from an upset customer. ...
- Question 304: A help desk technician inadvertently sent the credentials of...
- Question 305: An analyst reviews the following web server log entries: %2E...
- Question 306: A technician identifies a vulnerability on a server and appl...
- Question 307: An analyst is examining events in multiple systems but is ha...
- Question 308: When starting an investigation, which of the following must ...
- Question 309: Which of the following, BEST explains the function of TPM?...
- Question 310: Which of the following describes the reason Zero Trust shoul...
- Question 311: During an incident involving phishing, a security analyst ne...
- Question 312: A company's legal and accounting teams have decided it would...
- Question 313: SIMULATION You are a penetration tester who is reviewing the...

[×]
Download PDF File
Enter your email address to download CuramSoftware.CS0-003.v2026-09-21.q313.pdf