- Home
- CompTIA
- CompTIA PenTest+ Exam
- CompTIA.PT0-003.v2026-11-14.q190
- Question 135
Valid PT0-003 Dumps shared by ExamDiscuss.com for Helping Passing PT0-003 Exam! ExamDiscuss.com now offer the newest PT0-003 exam dumps, the ExamDiscuss.com PT0-003 exam questions have been updated and answers have been corrected get the newest ExamDiscuss.com PT0-003 dumps with Test Engine here:
Access PT0-003 Dumps Premium Version
(426 Q&As Dumps, 35%OFF Special Discount Code: freecram)
<< Prev Question Next Question >>
Question 135/190
SIMULATION 13
A penetration tester performs several Nmap scans against the web application for a client.
INSTRUCTIONS
Click on the WAF and servers to review the results of the Nmap scans. Then click on each tab to select the appropriate vulnerability and remediation options.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
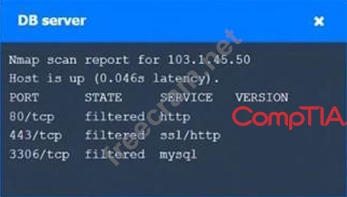
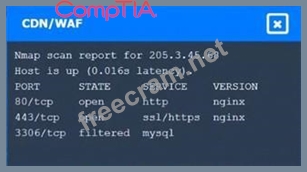
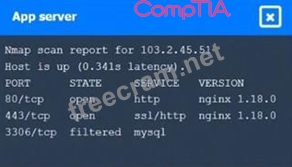

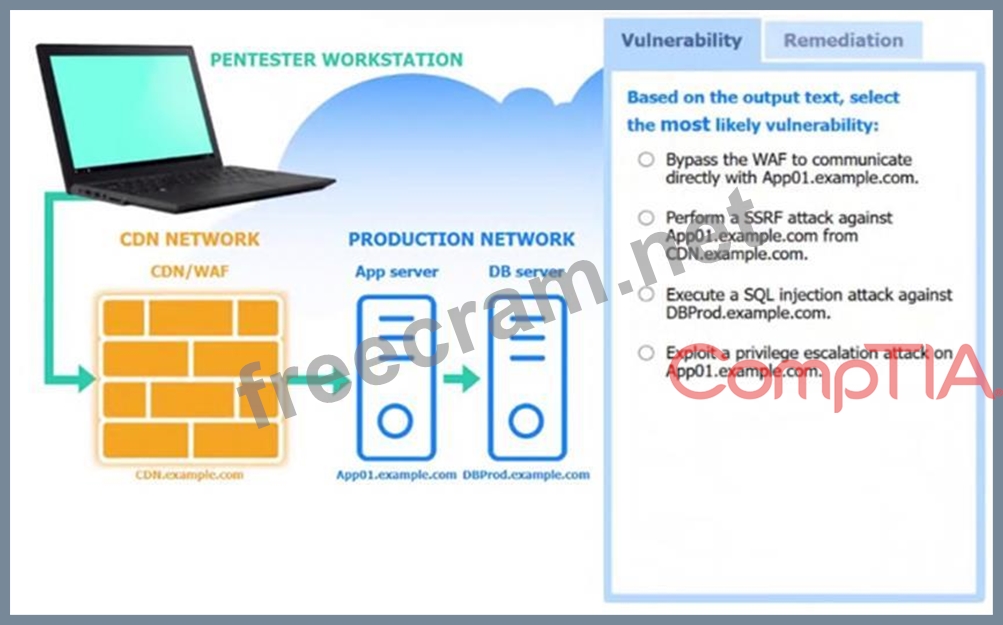
A penetration tester performs several Nmap scans against the web application for a client.
INSTRUCTIONS
Click on the WAF and servers to review the results of the Nmap scans. Then click on each tab to select the appropriate vulnerability and remediation options.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
Correct Answer:
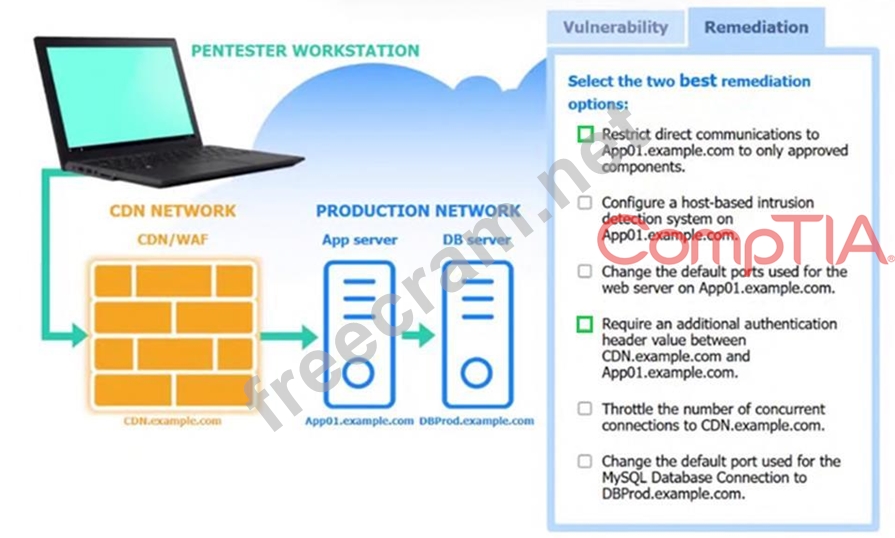
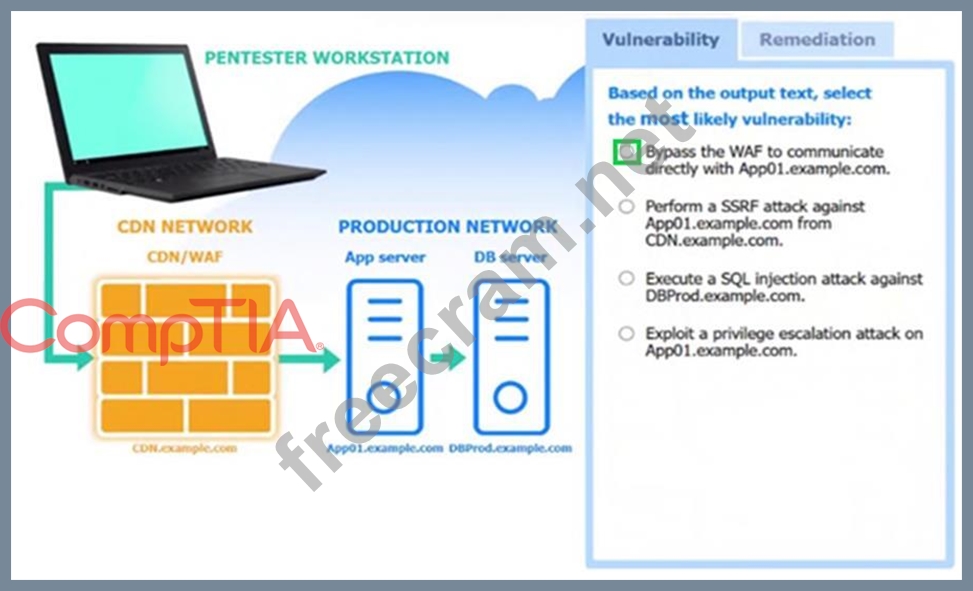
The scan shows App01.example.com has ports 80 and 443 open directly to the tester, meaning traffic can reach the application server without passing through the CDN/WAF. Restricting access to only the CDN/WAF and requiring a shared/authenticated header helps ensure requests must come through the approved front-end path.


- Question List (190q)
- Question 1: As part of an engagement, a penetration tester needs to scan...
- Question 2: A penetration tester is enumerating a Linux system. The goal...
- Question 3: A penetration tester is conducting a vulnerability scan. The...
- Question 4: While performing a penetration testing exercise, a tester ex...
- Question 5: A tester compromises a target host and then wants to maintai...
- Question 6: Which of the following is the part of a penetration test rep...
- Question 7: During an assessment, a penetration tester obtains access to...
- Question 8: A penetration tester runs a network scan and sees the follow...
- Question 9: A penetration tester would like to crack a hash using a list...
- Question 10: During host discovery, a security analyst wants to obtain Ge...
- Question 11: A penetration tester gains initial access to a Windows works...
- Question 12: A penetration tester gains access to a Linux system and crea...
- Question 13: A penetration tester wants to attack a server, exhausting it...
- Question 14: A penetration tester reviews a SAST vulnerability scan repor...
- Question 15: A penetration tester uses Hashcat to crack hashes discovered...
- Question 16: During a security assessment of an e-commerce website, a pen...
- Question 17: During a security assessment, a penetration tester captures ...
- Question 18: A penetration tester conducts reconnaissance for a client's ...
- Question 19: A penetration tester finished a security scan and uncovered ...
- Question 20: During a penetration test, a junior tester uses Hunter.io fo...
- Question 21: While performing an internal assessment, a tester uses the f...
- Question 22: A penetration tester has adversely affected a critical syste...
- Question 23: A penetration tester successfully clones a source code repos...
- Question 24: A penetration tester is performing a wireless assessment tha...
- Question 25: A penetration tester needs to complete cleanup activities fr...
- Question 26: During an engagement, a penetration tester needs to break th...
- Question 27: A penetration tester conducts reconnaissance and looks for w...
- Question 28: While conducting a peer review for a recent assessment, a pe...
- Question 29: A penetration tester writes a Bash script to automate the ex...
- Question 30: During a penetration test, a tester compromises a Windows co...
- Question 31: A penetration testing company is defining the rules of engag...
- Question 32: A penetration tester gains initial access to an endpoint and...
- Question 33: A penetration tester identifies multiple connections to publ...
- Question 34: A penetration tester compromises a Windows OS endpoint that ...
- Question 35: An organization's Chief Information Security Officer debates...
- Question 36: SIMULATION 6 A penetration tester performs several Nmap scan...
- Question 37: During a testing engagement, a penetration tester compromise...
- Question 38: During an internal engagement, a penetration tester compromi...
- Question 39: A penetration tester gains initial access to a system and ge...
- Question 40: During a vulnerability assessment, a penetration tester find...
- Question 41: During an engagement, a penetration tester discovers a web a...
- Question 42: A penetration tester wants to perform a SQL injection test. ...
- Question 43: During a security assessment, a penetration tester gains acc...
- Question 44: A penetration tester is conducting an assessment of offline ...
- Question 45: During a penetration test, the tester executes the following...
- Question 46: A penetration tester is authorized to perform a DoS attack a...
- Question 47: A penetration tester reviews a SAST vulnerability scan repor...
- Question 48: A penetration tester attempts to access an internet-facing w...
- Question 49: A tester conducts a web application penetration test and dis...
- Question 50: A penetration tester successfully gains access to a Linux sy...
- Question 51: A penetration tester performs an assessment on the target co...
- Question 52: A penetration tester is conducting reconnaissance on a targe...
- Question 53: A penetration tester has discovered sensitive files on a sys...
- Question 54: A penetration tester gains access to a domain member server ...
- Question 55: During an assessment, a penetration tester obtains a low-pri...
- Question 56: A penetration tester observes an employee logging in to thei...
- Question 57: During an assessment, a penetration tester runs the followin...
- Question 58: Which of the following components of a penetration test repo...
- Question 59: There is a low-level shell on a system, and a penetration te...
- Question 60: A penetration tester creates the following Python script tha...
- Question 61: A penetration tester needs to test a very large number of UR...
- Question 62: A penetration tester finds that an application responds with...
- Question 63: During an assessment, a penetration tester compromises some ...
- Question 64: Which of the following tools provides Python classes for int...
- Question 65: SIMULATION 10 A penetration tester has identified a series o...
- Question 66: A penetration testing team needs to determine whether it is ...
- Question 67: A penetration tester conducts a scan on an exposed Linux web...
- Question 68: A penetration tester wants to automatically enumerate all ci...
- Question 69: A penetration tester cannot use Nmap and must perform port d...
- Question 70: During an assessment, a penetration tester sends the followi...
- Question 71: During an assessment, a penetration tester gains access to o...
- Question 72: A penetration tester needs to evaluate the order in which th...
- Question 73: A penetration tester exploits a vulnerable service to gain a...
- Question 74: A tester wants to pivot from a compromised host to another n...
- Question 75: A security analyst reviews the following output while assess...
- Question 76: A penetration tester searches for an entry point into a clie...
- Question 77: SIMULATION 11 A security analyst is asked to perform various...
- Question 78: A tester needs to begin capturing WLAN credentials for crack...
- Question 79: A penetration tester gains access to a host but does not hav...
- Question 80: During an external penetration test, a tester receives the f...
- Question 81: During a wireless penetration assessment for a small busines...
- Question 82: A penetration tester conducts OSINT for a client and discove...
- Question 83: A penetration tester performs a service enumeration process ...
- Question 84: Which of the following is the most efficient way to infiltra...
- Question 85: During a security assessment for an internal corporate netwo...
- Question 86: Which of the following is most important when communicating ...
- Question 87: A penetration tester is attempting to exfiltrate sensitive d...
- Question 88: A penetration tester has found a web application that is run...
- Question 89: A penetration tester uses a Python script to enumerate open ...
- Question 90: A penetration tester gains access to a domain server and wan...
- Question 91: A penetration tester must gain entry to a client's office bu...
- Question 92: During a pre-engagement activity with a new customer, a pene...
- Question 93: A penetration tester obtains a regular domain user's set of ...
- Question 94: While conducting an assessment, a penetration tester identif...
- Question 95: Which of the following can an access control vestibule help ...
- Question 96: An external legal firm is conducting a penetration test of a...
- Question 97: Which of the following differentiates MITRE ATT&CK from ...
- Question 98: An internal penetration tester is on site assessing network ...
- Question 99: A penetration tester aims to exploit a vulnerability in a wi...
- Question 100: During a penetration test of a server application, a securit...
- Question 101: During a security assessment, a penetration tester wants to ...
- Question 102: During an internal penetration test, a tester compromises a ...
- Question 103: A company wants to perform a BAS (Breach and Attack Simulati...
- Question 104: During an engagement, a penetration tester wants to enumerat...
- Question 105: A penetration tester gains low-privilege shell access to a h...
- Question 106: A penetration tester is testing a power plant's network and ...
- Question 107: A penetration tester was able to capture the credentials for...
- Question 108: Which of the following are the most important considerations...
- Question 109: Which of the following frameworks can be used to classify th...
- Question 110: During a penetration test, the tester configures a sniffing ...
- Question 111: During a security audit, a penetration tester wants to explo...
- Question 112: Which of the following protocols would a penetration tester ...
- Question 113: A penetration tester is evaluating a company's cybersecurity...
- Question 114: A penetration tester wants to use the following Bash script ...
- Question 115: During a penetration test, the tester uses a vulnerability s...
- Question 116: A penetration tester noticed that an employee was using a wi...
- Question 117: After exploiting a vulnerability in an insecure service to g...
- Question 118: Which of the following will reduce the possibility of introd...
- Question 119: A penetration tester identifies the URL for an internal admi...
- Question 120: A penetration tester writes the following script to enumerat...
- Question 121: As part of an engagement, a penetration tester wants to main...
- Question 122: A penetration tester is configuring a vulnerability manageme...
- Question 123: Which of the following elements of a penetration test report...
- Question 124: A company hires a penetration tester to test the security im...
- Question 125: A penetration tester assesses a complex web application and ...
- Question 126: As part of a security audit, a penetration tester finds an i...
- Question 127: A penetration tester uses Burp Suite to send the following r...
- Question 128: A penetration tester wants to gather the names of potential ...
- Question 129: A penetration tester is conducting an assessment on a web ap...
- Question 130: The following table shows the findings of an application sec...
- Question 131: SIMULATION 5 A penetration tester has been provided with onl...
- Question 132: A penetration tester is trying to execute a post-exploitatio...
- Question 133: A penetration tester establishes an initial reverse shell in...
- Question 134: A penetration tester is hired to test a client's systems. Th...
- Question 135: SIMULATION 13 A penetration tester performs several Nmap sca...
- Question 136: A penetration tester gains access to a Linux computer system...
- Question 137: As part of active reconnaissance, penetration testers need t...
- Question 138: A penetration tester observes that an employee repeatedly at...
- Question 139: Testing and reporting activities are complete. A penetration...
- Question 140: During a penetration test for a client that has a diverse in...
- Question 141: A penetration tester is evaluating the security of a corpora...
- Question 142: A penetration tester discovers data to stage and exfiltrate....
- Question 143: A penetration tester needs to evaluate the order in which th...
- Question 144: Which of the following is a ROE component that provides a pe...
- Question 145: During an assessment, a penetration tester needs to perform ...
- Question 146: A penetration tester would like to leverage a CSRF vulnerabi...
- Question 147: A tester is working on an engagement that has evasion and st...
- Question 148: During the reconnaissance phase, a penetration tester collec...
- Question 149: After obtaining a reverse shell, a penetration tester identi...
- Question 150: While conducting OSINT, a penetration tester discovers the c...
- Question 151: Which of the following describes the process of determining ...
- Question 152: A penetration tester presents the following findings to stak...
- Question 153: During a red-team operation, a tester gains local administra...
- Question 154: During an assessment, a penetration tester runs the followin...
- Question 155: During an assessment, a penetration tester plans to gather m...
- Question 156: While engaged in a penetration testing exercise, the tester ...
- Question 157: The following file was obtained during reconnaissance: (Exhi...
- Question 158: During an assessment, a penetration tester runs the followin...
- Question 159: While conducting a reconnaissance activity, a penetration te...
- Question 160: Which of the following are valid reasons for including base,...
- Question 161: A penetration tester reviews a scan report and identifies a ...
- Question 162: A tester plans to perform an attack technique over a comprom...
- Question 163: A penetration tester is investigating a buffer overflow on t...
- Question 164: During an engagement, a junior penetration tester found a mu...
- Question 165: A penetration tester enters an invalid user ID on the login ...
- Question 166: A penetration tester observes the following output from an N...
- Question 167: A tester obtains access to an endpoint subnet and wants to m...
- Question 168: A penetration tester is working on an engagement in which a ...
- Question 169: A penetration tester identifies indicators that company empl...
- Question 170: A penetration tester finds it is possible to downgrade a web...
- Question 171: A penetration tester is getting ready to conduct a vulnerabi...
- Question 172: SIMULATION 2 You are a penetration tester running port scans...
- Question 173: During a REST API security assessment, a penetration tester ...
- Question 174: A penetration tester achieves shell access. The tester tries...
- Question 175: During an assessment, a penetration tester wants to extend t...
- Question 176: A tester runs an Nmap scan against a Windows server and rece...
- Question 177: A penetration tester is performing an assessment against a c...
- Question 178: A penetration tester wants to create a malicious QR code to ...
- Question 179: SIMULATION 4 INSTRUCTIONS Analyze the code segments to deter...
- Question 180: A company hires a penetration tester to perform an external ...
- Question 181: A penetration tester needs to enumerate domains, subdomains,...
- Question 182: During an assessment, a penetration tester wants to escalate...
- Question 183: A vulnerability assessor is looking to establish a baseline ...
- Question 184: A penetration tester is performing a cloud-based penetration...
- Question 185: A penetration tester is getting ready to conduct a vulnerabi...
- Question 186: A penetration tester identifies an exposed corporate directo...
- Question 187: A penetration tester is using OSINT to identify client email...
- Question 188: A penetration tester wants to send a specific network packet...
- Question 189: A penetration tester gained a foothold within a network. The...
- Question 190: Given the following output snippet that was generated during...
