Valid CAS-005 Dumps shared by ExamDiscuss.com for Helping Passing CAS-005 Exam! ExamDiscuss.com now offer the newest CAS-005 exam dumps, the ExamDiscuss.com CAS-005 exam questions have been updated and answers have been corrected get the newest ExamDiscuss.com CAS-005 dumps with Test Engine here:
Access CAS-005 Dumps Premium Version
(604 Q&As Dumps, 35%OFF Special Discount Code: freecram)
<< Prev Question Next Question >>
Question 28/267
A security architect needs to enable a container orchestrator for DevSecOps and SOAR initiatives. The engineer has discovered that several Ansible YAML files used for the automation of configuration management have the following content:
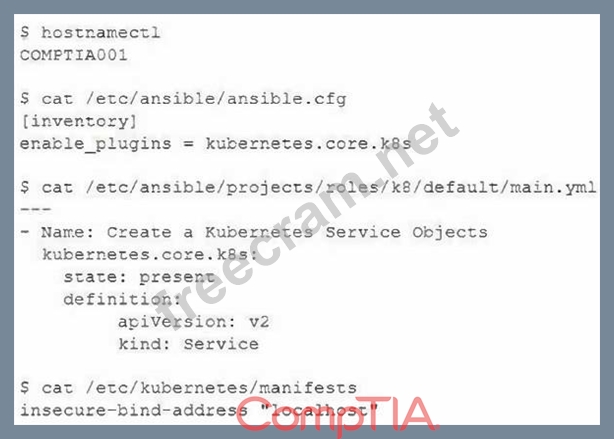
Which of the following should the engineer do to correct the security issues presented within this content?
Which of the following should the engineer do to correct the security issues presented within this content?
Correct Answer: D
The Ansible configuration file (/etc/ansible/ansible.cfg) contains an enable_plugins directive that allows Kubernetes modules to interact with Kubernetes resources. However, it does not enforce secure practices for managing these interactions, which could potentially expose sensitive data or allow unauthorized changes if not correctly configured or overly permissive.
The insecure configuration in the Ansible YAML file or the ansible.cfgfile should be reviewed or updated to enforce stricter security. Specifically, the configuration might inadvertently expose Kubernetes services to untrusted sources, and enabling plugins like kubernetes.core.k8s without sufficient control could lead to vulnerabilities.
Updating or removing the ansible.cfgfile ensures that secure defaults are applied, or more secure plugin configurations can be explicitly added, addressing the underlying issue.
The insecure configuration in the Ansible YAML file or the ansible.cfgfile should be reviewed or updated to enforce stricter security. Specifically, the configuration might inadvertently expose Kubernetes services to untrusted sources, and enabling plugins like kubernetes.core.k8s without sufficient control could lead to vulnerabilities.
Updating or removing the ansible.cfgfile ensures that secure defaults are applied, or more secure plugin configurations can be explicitly added, addressing the underlying issue.


- Question List (267q)
- Question 1: After a company discovered a zero-day vulnerability in its V...
- Question 2: During a review of the email security solution, a security a...
- Question 3: A security architect is troubleshooting an issue with an OID...
- Question 4: A security engineer must implement controls to limit access ...
- Question 5: A security architect is implementing a SOAR solution in an o...
- Question 6: An engineer is designing a solution that addresses the follo...
- Question 7: While performing mandatory monthly patch updates on a produc...
- Question 8: A mobile administrator is reviewing the following mobile dev...
- Question 9: As part of a new software development method, a program mana...
- Question 10: A global manufacturing company has an internal application t...
- Question 11: A company moved its on-premises services to the cloud. Altho...
- Question 12: An organization is implementing advanced security controls a...
- Question 13: A security analyst received a notification from a cloud serv...
- Question 14: A security architect for a global organization with a distri...
- Question 15: A security architect performs a baseline review on the SIEM....
- Question 16: A security engineer discovers that some workstations are try...
- Question 17: After a penetration test on the internal network the followi...
- Question 18: A threat intelligence company's business objective is to all...
- Question 19: A healthcare system recently suffered from a ransomware inci...
- Question 20: A company must meet the following security requirements when...
- Question 21: A network security architect is working on capturing network...
- Question 22: Previously intercepted communications must remain secure eve...
- Question 23: A security architect recommends replacing the company's mono...
- Question 24: A company is developing an application that will be used to ...
- Question 25: After an increase in adversarial activity, a company wants t...
- Question 26: A security engineer is performing threat modeling for an AI ...
- Question 27: A company needs to quickly assess whether software deployed ...
- Question 28: A security architect needs to enable a container orchestrato...
- Question 29: A security engineer is developing a solution to meet the fol...
- Question 30: A company updates its cloud-based services by saving infrast...
- Question 31: A systems engineer is configuring SSO for a business that wi...
- Question 32: A security analyst is assessing a new application written in...
- Question 33: A security engineer wants to stay up-to-date on new detectio...
- Question 34: A company needs to define a new road map for improving secur...
- Question 35: An organization decides to move to a distributed workforce m...
- Question 36: A security engineer is reviewing a security incident in whic...
- Question 37: While investigating an email server that crashed, an analyst...
- Question 38: A nation-state actor is exposed for attacking large corporat...
- Question 39: A security engineer would like to control configurations on ...
- Question 40: A security operations analyst is reviewing network traffic b...
- Question 41: A security administrator has isolated a computer system beca...
- Question 42: A pharmaceutical company employs automated control systems t...
- Question 43: The Chief Information Security Officer of a large multinatio...
- Question 44: A Chief Information Security Officer receives the following ...
- Question 45: An organization has several systems deployed in a public clo...
- Question 46: A systems administrator wants to reduce the number of failed...
- Question 47: An organization's vulnerability management team is reviewing...
- Question 48: A systems engineer is configuring a system baseline for serv...
- Question 49: A SOC engineer is designing a solution to automate a sequenc...
- Question 50: A malware analyst must examine the following partial file sa...
- Question 51: Which of the following best describes the reason a network a...
- Question 52: Which of the following best explains the importance of deter...
- Question 53: An engineering team determines the cost to mitigate certain ...
- Question 54: A security architect wants to ensure a remote host's identit...
- Question 55: During a recent assessment, a security analyst observed the ...
- Question 56: After an incident occurred, a team reported during the lesso...
- Question 57: A security architect discovers the following while reviewing...
- Question 58: Which of the following best describes a common use case for ...
- Question 59: A compliance officer is reviewing the data sovereignty laws ...
- Question 60: A security analyst is reviewing a SIEM and generates the fol...
- Question 61: A security officer is receiving alerts from a cloud service ...
- Question 62: A company is adopting microservice architecture in order to ...
- Question 63: In order to follow new regulations, the Chief Information Se...
- Question 64: An auditor is reviewing the logs from a web application to d...
- Question 65: A security architect wants to configure a mail server so it ...
- Question 66: An organization determined its preparedness for a ransomware...
- Question 67: A company is migrating its data center to the cloud. Some ho...
- Question 68: An organization is prioritizing efforts to remediate or miti...
- Question 69: A manufacturing plant is updating its IT services. During di...
- Question 70: During a security assessment, a penetration tester executed ...
- Question 71: A security architect examines a section of code and discover...
- Question 72: During a gap assessment, an organization notes that BYOD usa...
- Question 73: After remote desktop capabilities were deployed in the envir...
- Question 74: An organization is developing an in-house software platform ...
- Question 75: A company needs a highly secure method to transfer documents...
- Question 76: Which of the following items should be included when craftin...
- Question 77: During a vulnerability assessment, a scan reveals the follow...
- Question 78: A security audit of a company's application finds that custo...
- Question 79: After an incident response exercise, a security administrato...
- Question 80: An organization has a hybrid architecture that requires disp...
- Question 81: Which of the following utilizes policies that route packets ...
- Question 82: Company A acquired Company B and needs to determine how the ...
- Question 83: A company needs to increase the maturity level for the cyber...
- Question 84: A regulated company is in the process of refreshing its enti...
- Question 85: A company needs to create a design that facilitates monitori...
- Question 86: An organization wants to create a threat model to identity v...
- Question 87: A security operation analyst is reviewing the following log ...
- Question 88: An endpoint security engineer finds that a newly acquired co...
- Question 89: A company is having issues with its vulnerability management...
- Question 90: An analyst has prepared several possible solutions to a succ...
- Question 91: A company discovers intellectual property data on commonly k...
- Question 92: SIMULATION An incident occurred at Site A when an attacker s...
- Question 93: SIMULATION During the course of normal SOC operations, three...
- Question 94: A retail organization wants to properly test and verify its ...
- Question 95: A government agency implements a configuration that disables...
- Question 96: A user reports application access issues to the help desk. T...
- Question 97: A security engineer is creating a single CSR for the followi...
- Question 98: A systems administrator works with engineers to process and ...
- Question 99: A security administrator is performing a gap assessment agai...
- Question 100: A company purchased Burp Suite licenses this year for each a...
- Question 101: A company is concerned about the security of customer data. ...
- Question 102: A hospital's requirements for remote third-party monitoring ...
- Question 103: A systems administrator wants to introduce a newly released ...
- Question 104: To bring digital evidence in a court of law, the evidence mu...
- Question 105: An organization receives intelligence information about a fo...
- Question 106: An organization recently implemented a purchasing freeze tha...
- Question 107: A security engineer needs 10 secure the OT environment based...
- Question 108: A security team determines that the most significant risks w...
- Question 109: A security operations engineer needs to prevent inadvertent ...
- Question 110: To prevent data breaches, security leaders at a company deci...
- Question 111: A systems administrator wants to use existing resources to a...
- Question 112: During an incident response activity, the response team coll...
- Question 113: A cybersecurity architect is reviewing the detection and mon...
- Question 114: John Doe's email account was compromised. The attacker's acc...
- Question 115: An organization wants to implement a secure cloud architectu...
- Question 116: A software company deployed a new application based on its i...
- Question 117: A software development company wants to ensure that users ca...
- Question 118: All organization is concerned about insider threats from emp...
- Question 119: A reverse engineer is analyzing a malware sample from a rece...
- Question 120: A security analyst discovers a new device on the company's d...
- Question 121: A company detects suspicious activity associated with inboun...
- Question 122: An administrator needs to craft a single certificate-signing...
- Question 123: A company undergoing digital transformation is reviewing the...
- Question 124: A programmer is reviewing the following proprietary piece of...
- Question 125: A security architect must implement security controls in a s...
- Question 126: Engineers are unable to control pumps at Site A from Site B ...
- Question 127: A global organization is reviewing potential vendors to outs...
- Question 128: An architect is securing an external infrastructure to suppo...
- Question 129: A company recently migrated its critical web application to ...
- Question 130: After discovering that an employee is using a personal lapto...
- Question 131: After a leak of important documents, a company decides to im...
- Question 132: An organization recently migrated data to a new file managem...
- Question 133: Protected company data was recently exfiltrated. The SOC did...
- Question 134: A company developed a new solution that needs to track any c...
- Question 135: A company sells a security appliance assembled from globally...
- Question 136: A software development company needs to mitigate third-party...
- Question 137: Which of the following most likely explains the reason a sec...
- Question 138: A company is preparing to move a new version of a web applic...
- Question 139: An organization has been using self-managed encryption keys ...
- Question 140: A security officer performs due diligence activities before ...
- Question 141: A SOC analyst must perform threat-modeling activities for a ...
- Question 142: In a recent audit, several critical legacy systems, which ar...
- Question 143: An engineer has had scaling issues with a web application ho...
- Question 144: Which of the following enables the meaningful manipulation o...
- Question 145: An organization found a significant vulnerability associated...
- Question 146: An organization has deployed a cloud-based application that ...
- Question 147: A threat hunter is identifying potentially malicious activit...
- Question 148: A local government that is investigating a data exfiltration...
- Question 149: Which of the following best describes the advantage of homom...
- Question 150: A CRM company leverages a CSP PaaS service to host and publi...
- Question 151: A pharmaceutical company uses a cloud provider to host thous...
- Question 152: A security analyst is performing a review of a web applicati...
- Question 153: A security engineer receives an alert from the SIEM platform...
- Question 154: A security engineer is reviewing event logs because an emplo...
- Question 155: During a penetration test, several users report that certain...
- Question 156: Which of the following key management practices ensures that...
- Question 157: An organization currently has IDS, firewall, and DLP systems...
- Question 158: A company receives several complaints from customers regardi...
- Question 159: A company wants to implement hardware security key authentic...
- Question 160: A security researcher tells a company that one of its soluti...
- Question 161: An administrator brings the company's fleet of mobile device...
- Question 162: Which of the following best describes the challenges associa...
- Question 163: A company recently acquired a SaaS company and performed a g...
- Question 164: Company A is merging with Company B. Company A is a small, l...
- Question 165: A company that uses several cloud applications wants to prop...
- Question 166: A vulnerability scan was performed on a website, and the fol...
- Question 167: A news organization wants to implement workflows that allow ...
- Question 168: The information security manager at a 24-hour manufacturing ...
- Question 169: A security administrator needs to develop a remediation plan...
- Question 170: An enterprise is deploying APIs that utilize a private key a...
- Question 171: A company must build and deploy security standards for all s...
- Question 172: An organization hires a security consultant to establish a S...
- Question 173: An organization is deploying a new data lake that will centr...
- Question 174: During a vendor assessment, an analyst reviews a listing of ...
- Question 175: A compliance manager is planning an engagement to identify r...
- Question 176: Source code snippets for two separate malware samples are sh...
- Question 177: A company's SIEM is continuously reporting false positives a...
- Question 178: A company created an external application for its customers....
- Question 179: A company SIEM collects information about the log sources. G...
- Question 180: An external SaaS solution user reports a bug associated with...
- Question 181: A security engineer is assessing a new tool to segment data ...
- Question 182: A security engineer reviews an after-action report from a pr...
- Question 183: A company runs a DAST scan on a web application. The tool ou...
- Question 184: A company recently deployed new servers to create an additio...
- Question 185: The security team is looking into aggressive bot behavior th...
- Question 186: An analyst needs to evaluate all images and documents that a...
- Question 187: The device event logs sourced from MDM software are as follo...
- Question 188: A company designs policies and procedures for hardening cont...
- Question 189: A security technician is investigating a system that tracks ...
- Question 190: A Chief Information Security Officer requests an action plan...
- Question 191: A senior cybersecurity engineer is solving a digital certifi...
- Question 192: A Chief Information Security Officer assigns a team to creat...
- Question 193: Which of the following best describes the reason PQC prepara...
- Question 194: A system of globally distributed certificate servers connect...
- Question 195: A game developer wants to reach new markets and is advised b...
- Question 196: A small number but steady series of attempts to breach the n...
- Question 197: An organization's load balancers have reached EOL and are sc...
- Question 198: A financial services organization is using AI to fully autom...
- Question 199: A university issues badges through a homegrown identity mana...
- Question 200: After some employees are caught uploading data to online per...
- Question 201: A security manager has written an incident response playbook...
- Question 202: The results of an internal audit indicate several employees ...
- Question 203: A security architect wants to prevent security impacts from ...
- Question 204: A malicious actor exploited firmware vulnerabilities and use...
- Question 205: A security engineer discovers that some legacy systems are s...
- Question 206: A security architect is implementing more restrictive polici...
- Question 207: A company experienced a data breach, resulting in the disclo...
- Question 208: An application security engineer is examining the IAM config...
- Question 209: A security analyst receives the following SIEM alert for rev...
- Question 210: A company is planning to migrate all of its on-site-hosted a...
- Question 211: A security analyst is performing threat modeling for a new A...
- Question 212: A security analyst reviews network logs and notices a large ...
- Question 213: A security administrator wants to detect a potential forged ...
- Question 214: A software developer is working on a piece of code required ...
- Question 215: Based on the results of a SAST report on a legacy applicatio...
- Question 216: A water power generation plant fails a security inspection. ...
- Question 217: Which of the following AI concerns is most adequately addres...
- Question 218: A penetration tester is drafting a report of findings and re...
- Question 219: A company is migrating from company-owned phones to a BYOD s...
- Question 220: A security architect is performing threat-modeling activitie...
- Question 221: A developer needs to improve the cryptographic strength of a...
- Question 222: Which of the following explains why an organization should c...
- Question 223: A security engineer needs to select the architecture for a c...
- Question 224: An analyst is using the Diamond Model of Intrusion Analysis ...
- Question 225: A multinational enterprise is planning to implement a centra...
- Question 226: A cloud engineer wants to configure mail security protocols ...
- Question 227: A company wants to prevent a partner company from denying ag...
- Question 228: A Chief Information Security Officer is concerned about the ...
- Question 229: A company is decommissioning old servers and hard drives tha...
- Question 230: A security analyst is designing a touch screen device so use...
- Question 231: A company's BIA indicates that any loss of more than one hou...
- Question 232: During an audit at an organization, auditors find that devel...
- Question 233: A cyberanalyst has been tasked with recovering PDF files fro...
- Question 234: A company's help desk is experiencing a large number of call...
- Question 235: A cloud security architect has been tasked with finding a so...
- Question 236: A junior developer is informed about the impact of new malwa...
- Question 237: The material findings from a recent compliance audit indicat...
- Question 238: A building camera is remotely accessed and disabled from the...
- Question 239: SIMULATION A security engineer needs to review the configura...
- Question 240: A firewall administrator needs to ensure all traffic across ...
- Question 241: As part of a security audit in the software development life...
- Question 242: A security analyst was monitoring the networks of a group of...
- Question 243: A security engineer receives an alert from the threat intell...
- Question 244: A security consultant recommends that a solution be deployed...
- Question 245: A security engineer is reviewing the SIEM logs after a serve...
- Question 246: During post-incident analysis of a recent website outage, an...
- Question 247: A company runs a DAST scan on a web application. The tool ou...
- Question 248: A security officer received several complaints from users ab...
- Question 249: A company hosts a platform-as-a-service solution with a web-...
- Question 250: After a recent outage, a software engineering company perfor...
- Question 251: A company hired a third-party consultant to run a cybersecur...
- Question 252: An organization purchased a new manufacturing facility and t...
- Question 253: A Chief Information Security Officer (CISO) is developing a ...
- Question 254: A penetration tester discovers a condition that causes unexp...
- Question 255: Which of the following is the best reason for obtaining file...
- Question 256: A security administrator at a global organization wants to u...
- Question 257: A company established a new process for business analysts to...
- Question 258: Which of the following is the best way to protect the websit...
- Question 259: The security team is receiving escalated support tickets sta...
- Question 260: A security engineer is reviewing logs and summarizes the fol...
- Question 261: Which of the following is the reason why security engineers ...
- Question 262: While investigating a security event an analyst finds eviden...
- Question 263: Which of the following describes how a risk assessment is pe...
- Question 264: A systems administrator is working with clients to verify em...
- Question 265: A company's headquarters is in an area with a high rate of s...
- Question 266: A company plans to implement a research facility with intell...
- Question 267: While performing threat-hunting functions, an analyst is usi...
