- Home
- Cisco
- Developing Applications using Cisco Core Platforms and APIs (DEVCOR)
- Cisco.350-901.v2026-06-12.q252
- Question 55
Valid 350-901 Dumps shared by EduDump.com for Helping Passing 350-901 Exam! EduDump.com now offer the newest 350-901 exam dumps, the EduDump.com 350-901 exam questions have been updated and answers have been corrected get the newest EduDump.com 350-901 dumps with Test Engine here:
Access 350-901 Dumps Premium Version
(667 Q&As Dumps, 35%OFF Special Discount Code: freecram)
<< Prev Question Next Question >>
Question 55/252
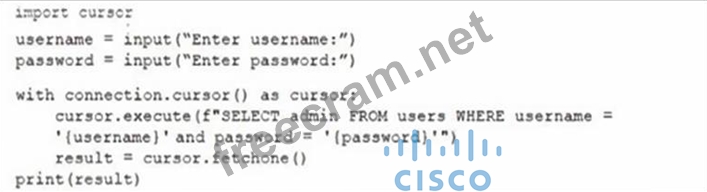
Refer to the exhibit. A network engineer writes Python code for a web application to query an SQL database. The code is vulnerable to SQL injection attacks. Which command must the engineer enter into the username input to exploit the vulnerability?
Correct Answer: C
The provided Python code directly concatenates user input into an SQL query, making it vulnerable to SQL injection. The malicious input '; select true; --'can be used to bypass authentication by closing the original query and appending a new condition that always evaluates to true (select true).
';closes the first query statement.
select true;injects a new query that always returns a valid result.
--is a comment that ignores the rest of the query, preventing SQL errors.
';closes the first query statement.
select true;injects a new query that always returns a valid result.
--is a comment that ignores the rest of the query, preventing SQL errors.


- Question List (252q)
- Question 1: A new record-keeping application for employees to track cust...
- Question 2: Drag and Drop Question Drag and drop the code from the botto...
- Question 3: Drag and Drop Question Drag and drop the code from the botto...
- Question 4: Refer to the exhibit. Interface Loopback 1 must be created w...
- Question 5: Drag and Drop Question An application is being built to coll...
- Question 6: A local Docker container with a Container ID of 391441516e7a...
- Question 7: What is a characteristic of a monolithic architecture?...
- Question 8: A developer needs to configure an environment to orchestrate...
- Question 9: Drag and Drop Question Click on the resource tabs in the top...
- Question 10: Refer to the exhibit. Pipenv is used to manage dependencies....
- Question 11: Drag and Drop Question Refer to the exhibit. Drag and drop t...
- Question 12: Drag and Drop Question Drag and drop the code snippets from ...
- Question 13: What are two benefits of using distributed log collectors? (...
- Question 14: Drag and Drop Question Drag and drop the steps on the left i...
- Question 15: Refer to the exhibit. The engineer runs this code and notice...
- Question 16: An enterprise refactors its monolithic application into a mo...
- Question 17: Refer to the exhibits. An application is created to serve th...
- Question 18: Which two methods are API security best practices? (Choose t...
- Question 19: Which interface provides an IOx application on a Catalyst 90...
- Question 20: What is a requirement of the dev/prod parity principle of th...
- Question 21: What is a benefit of using a dependency management tool in s...
- Question 22: How should a web application be designed to work on a platfo...
- Question 23: Refer to the exhibit. Which URI string retrieves configured ...
- Question 24: Drag and Drop Question Refer to the exhibit. Drag and drop t...
- Question 25: To complete the Python script to enable the SSID with a name...
- Question 26: Drag and Drop Question Drag and drop the code from the botto...
- Question 27: Which two data encoding techniques are supported by gRPC? (C...
- Question 28: Refer to the exhibit. a developer created the code, but it f...
- Question 29: Drag and Drop Question Refer to the exhibit. A system admini...
- Question 30: A DevOps engineer needs to design an application to send ema...
- Question 31: How is AppDynamics used to instrument an application?...
- Question 32: Refer to the exhibit. The Python code is used to retrieve da...
- Question 33: Refer to the exhibit. A network engineer developed an Ansibl...
- Question 34: Refer to the exhibit. An application is created to serve an ...
- Question 35: Which two files are needed to create a Cisco IOx application...
- Question 36: Refer to the exhibit. The JSON response is received from the...
- Question 37: What is submitted when an SSL certificate is requested?...
- Question 38: A developer has created a local Docker alpine image that has...
- Question 39: Drag and Drop Question Drag and drop the steps from the left...
- Question 40: An application requires SSL certificates signed by an interm...
- Question 41: What is the unique identifier in the OAuth2 three-legged aut...
- Question 42: Which OAuth mechanism enables clients to continue to have an...
- Question 43: Refer to the exhibit. An application was created to serve mu...
- Question 44: What is the purpose of the OAuth2 three-legged authorization...
- Question 45: Refer to the exhibit. Which code snippet completes this code...
- Question 46: Drag and Drop Question A developer is creating a Python Flas...
- Question 47: A web application is susceptible to cross-site scripting. Wh...
- Question 48: Refer to the exhibit. The presented application consists of ...
- Question 49: An engineer oversees the development of an application that ...
- Question 50: Refer to the exhibit. An engineer needs to provide code that...
- Question 51: A container running a Python script is failing when it reach...
- Question 52: Drag and Drop Question Refer to the exhibit. Drag and drop t...
- Question 53: What is a reason to choose global load-balancing instead of ...
- Question 54: Refer to the exhibit. An engineer needs to change the IP add...
- Question 55: Refer to the exhibit. A network engineer writes Python code ...
- Question 56: Refer to the exhibit. Information was obtained by using REST...
- Question 57: From which type of device is model-driven development able t...
- Question 58: Drag and Drop Question Drag and drop the code snippets from ...
- Question 59: Refer to the exhibit. Which set of API requests must be exec...
- Question 60: Which two principles are included in the codebase tenet of t...
- Question 61: Drag and Drop Question Drag and Drop the application require...
- Question 62: Drag and Drop Question Drag and drop the code from the botto...
- Question 63: An organization manages a large cloud-deployed application t...
- Question 64: An engineer needs to improve the responsiveness of an applic...
- Question 65: Drag and Drop Question Drag and drop the steps from the left...
- Question 66: Drag and Drop Question Drag and drop the code from the botto...
- Question 67: Drag and Drop Question Drag and drop the code snippets from ...
- Question 68: Drag and Drop Question Drag and drop the code from the botto...
- Question 69: Which action enhances end-user privacy when an application i...
- Question 70: What is an advantage of using gRPC dial-in when using model-...
- Question 71: A developer is working on a live project and must apply a ne...
- Question 72: Refer to the exhibit. A developer wants to automatically dep...
- Question 73: Drag and Drop Question Drag and drop the code snippets from ...
- Question 74: Drag and Drop Question Refer to the exhibit. Drag and drop t...
- Question 75: Refer to the exhibit. Two editors are concurrently updating ...
- Question 76: Refer to the exhibit. A Python API server has been deployed....
- Question 77: Drag and Drop Question An engineer sets up two tasks in an A...
- Question 78: While developing an application following the 12-factor app ...
- Question 79: A web application has those requirements for HTTP cache cont...
- Question 80: Drag and Drop Question Drag and drop the code snippets from ...
- Question 81: An engineer is developing an application to use across organ...
- Question 82: Drag and Drop Question Refer to the exhibit. Drag and drop t...
- Question 83: Drag and Drop Question Refer to the exhibit. Drag and drop t...
- Question 84: Refer to the exhibit. An application stopped responding whil...
- Question 85: Refer to the exhibit. Which action will complete the workflo...
- Question 86: The UCS Python SDK includes modules for Service Profile temp...
- Question 87: Drag and Drop Question Drag and drop the code from the botto...
- Question 88: A developer has built a Docker image named 'devcor12a3b45678...
- Question 89: Which two strategies are used to protect personally identifi...
- Question 90: Refer to the exhibit. An application was developed to be dep...
- Question 91: Which step is part of a three-legged OAuth2 authorization co...
- Question 92: What is a capability of the End User Monitoring feature of t...
- Question 93: Drag and Drop Question Refer to the exhibit. Drag and drop t...
- Question 94: A user is receiving a 429 Too Many Requests error. Which sch...
- Question 95: Refer to the exhibit. As part of the Ansible playbook workfl...
- Question 96: Drag and Drop Question Refer to the exhibit. Drag and drop t...
- Question 97: A developer checks out a branch named feat23 from a Git repo...
- Question 98: An application has initiated an OAuth authorization code gra...
- Question 99: Drag and Drop Question Refer to the exhibit. Drag and drop t...
- Question 100: Drag and Drop Question A developer must containerize a Pytho...
- Question 101: Into which two areas are AppDynamics APIs categorized? (Choo...
- Question 102: What is a data privacy concern when designing data storage?...
- Question 103: Drag and Drop Question Refer to the exhibit. Drag and drop t...
- Question 104: Refer to the exhibit. A developer must create a new network ...
- Question 105: Refer to the exhibit. An engineer is managing a network that...
- Question 106: Drag and Drop Question Drag and drop the code snippets from ...
- Question 107: Which authorization steps are required to obtain an access t...
- Question 108: Which command is used to enable application hosting on a Cis...
- Question 109: A development team is considering options for implementing a...
- Question 110: Drag and Drop Question Drag and drop the code snippets from ...
- Question 111: An engineer must enable an SSID in a Meraki network. Which r...
- Question 112: Which action reduces latency in a microservices application?...
- Question 113: Refer to the exhibit. The YAML represented is using the ios_...
- Question 114: What is the result of a successful OAuth2 authorization gran...
- Question 115: A company must adopt a configuration management solution for...
- Question 116: A developer is working in a branch to develop a new feature ...
- Question 117: Refer to the exhibit. A Docker swarm service is currently ru...
- Question 118: What is a benefit of running multiple instances of a back-en...
- Question 119: Refer to the exhibit. A devops engineer activates an intent-...
- Question 120: A media streaming company uses a cloud-based microservices a...
- Question 121: A heterogeneous network of vendors and device types needs au...
- Question 122: Drag and Drop Question Drag and drop the code from the botto...
- Question 123: A developer in a team of distributed authors is working on c...
- Question 124: Drag and Drop Question Refer to the exhibit above and click ...
- Question 125: A developer deployed a web application in a local data cente...
- Question 126: Drag and Drop Question Drag and drop the code from the botto...
- Question 127: Refer to the exhibit. An engineer creates an application tha...
- Question 128: A custom dashboard of the network health must be created by ...
- Question 129: Refer to the exhibit. Which URL retrieves the errors in the ...
- Question 130: Refer to the exhibit. A network engineer created a simple Py...
- Question 131: Which approach is part of the twelve-factor app methodology?...
- Question 132: A developer has issued the git add file1 file2 test.py comma...
- Question 133: Drag and Drop Question Drag and drop the code from the botto...
- Question 134: Drag and Drop Question Drag and drop the code from the botto...
- Question 135: Drag and Drop Question Drag and drop the code from the botto...
- Question 136: Which transport layer protocol does gRPC use to retrieve tel...
- Question 137: Refer to the exhibit. An engineer must add a new loopback in...
- Question 138: Refer to the exhibit. The information in the exhibit was obt...
- Question 139: A development team is looking for a tool to automate configu...
- Question 140: Drag and Drop Question Refer to the exhibit. Drag and drop t...
- Question 141: Refer to the exhibit. A developer has created a Python scrip...
- Question 142: Refer to the exhibit. Which command publishes the Docker ima...
- Question 143: Drag and Drop Question A developer is designing an applicati...
- Question 144: What is a benefit of using continuous testing and static cod...
- Question 145: Refer to the exhibit. An architect wrote an application to c...
- Question 146: Which function does Fluentd fulfill for application logging ...
- Question 147: Which snippet presents the correct API call to configure, se...
- Question 148: In an event-driven architecture-based system, what is a char...
- Question 149: Drag and Drop Question A developer is creating a Python scri...
- Question 150: A developer is developing a microservices code to manage RES...
- Question 151: Drag and Drop Question Refer to the exhibit. Drag and drop t...
- Question 152: Refer to the exhibit. Which RESTCONF verb changes the Gigabi...
- Question 153: A developer plans to create a new bugfix branch to fix a bug...
- Question 154: Drag and Drop Question Drag and drop the code from the botto...
- Question 155: An engineer is developing an application that must store the...
- Question 156: Drag and Drop Question Drag and drop the code snippets from ...
- Question 157: When a Cisco IOS XE networking device is configured using RE...
- Question 158: Refer to the exhibit. An engineer writes a script to retriev...
- Question 159: Refer to the exhibit. An application is being developed as a...
- Question 160: A heterogeneous network of vendors and device types needs au...
- Question 161: Which two countermeasures help reduce the risk of playback a...
- Question 162: Refer to the exhibit. An engineer implements a Flask-based A...
- Question 163: Refer to the exhibit. An engineer is automating network devi...
- Question 164: Drag and Drop Question Drag and drop the descriptions from t...
- Question 165: Refer to the exhibit. The Ansible playbook is using the netc...
- Question 166: Which solution is used to manage automatic dependencies on a...
- Question 167: When an application is designed that requires high availabil...
- Question 168: What is a well-defined concept of GDPR compliance?...
- Question 169: Refer to the exhibit. A Python script needs to catch errors ...
- Question 170: Drag and Drop Question A Python application is being written...
- Question 171: A developer creates an application for a Cisco Catalyst 9000...
- Question 172: Refer to the exhibit above and click on the IETF Routing tab...
- Question 173: Refer to the exhibit. Which cURL request is included in the ...
- Question 174: Drag and Drop Question Drag and drop the code snippets from ...
- Question 175: Which tow actions must be taken when an observable microserv...
- Question 176: Drag and Drop Question Refer to the exhibit. Drag and drop t...
- Question 177: A team is developing a cloud-native application for network ...
- Question 178: Which telemetry transport option allows the desired configur...
- Question 179: Refer to the exhibit. Which word is missing from this Ansibl...
- Question 180: A developer has updated an application to fix a bug with the...
- Question 181: In the three-legged OAuth2 process, after the authorization ...
- Question 182: An engineer is responsible for managing the infrastructure a...
- Question 183: Which two design considerations should be considered when bu...
- Question 184: Drag and Drop Question Refer to the exhibit above and click ...
- Question 185: Drag and Drop Question Drag and drop the code snippets from ...
- Question 186: Refer to the exhibit. Which command resolves the merge confl...
- Question 187: Drag and Drop Question Refer to the above and click on the r...
- Question 188: Drag and Drop Question Drag and drop the code from the botto...
- Question 189: Refer to the exhibit. A developer needs to find the geograph...
- Question 190: Drag and Drop Question Drag and drop the code from the botto...
- Question 191: Refer to the exhibit. An application has been developed to s...
- Question 192: Refer to the exhibit. A developer must review an intern's co...
- Question 193: Which load balancing algorithm balances load based on the ac...
- Question 194: Refer to the exhibit. A developer runs the docker service sc...
- Question 195: Refer to the exhibit. A network engineer needs to handle API...
- Question 196: Drag and Drop Question Drag and drop the code from the botto...
- Question 197: Drag and Drop Question A developer is creating a Python scri...
- Question 198: A company has written a script that creates a log bundle fro...
- Question 199: Drag and Drop Question Drag and drop the operations from the...
- Question 200: What are two capabilities of AppDynamics when instrumenting ...
- Question 201: Drag and Drop Question Refer to the exhibit. Python threadin...
- Question 202: Which statement about microservices architecture is true?...
- Question 203: Drag and Drop Question Refer to the exhibit above and click ...
- Question 204: Refer to the exhibit. The Dockerfile is placed in the curren...
- Question 205: The response from a server includes the header ETag: W/"7eb8...
- Question 206: What are two building blocks of the 12-factor app? (Choose t...
- Question 207: Which Git command enables the developer to revert back to f4...
- Question 208: Refer to the exhibit. Which action resolves the error for th...
- Question 209: An engineer is developing a client/server application for us...
- Question 210: Drag and Drop Question Refer to the exhibit. A developer is ...
- Question 211: Drag and Drop Question Drag and drop the code from the botto...
- Question 212: Drag and Drop Question Drag and drop the code snippets from ...
- Question 213: Why is end-to-end encryption deployed when exposing sensitiv...
- Question 214: A developer has just completed the configuration of an API t...
- Question 215: An architect must optimize traffic that targets a popular AP...
- Question 216: Drag and Drop Question Drag and drop the code from the botto...
- Question 217: A company is using an API to share sensitive customer data w...
- Question 218: The Meraki API URL https://api.meraki.com/api/v0/networks/12...
- Question 219: Refer to the exhibit. Which command results in a detached HE...
- Question 220: An engineer wants to design an application that meets these ...
- Question 221: Refer to the exhibit. An engineer needs to configure an inte...
- Question 222: A development team is looking for a tool to automate configu...
- Question 223: Which configuration stop must be performed on a Cisco IOS XE...
- Question 224: What is the gRPC Network Management Interface protocol?...
- Question 225: Refer to the exhibit. A software engineer develops an applic...
- Question 226: A company is starting a machine-learning project to analyze ...
- Question 227: Drag and Drop Question Drag and drop the code snippets from ...
- Question 228: Refer to the exhibit. An application is developed to perform...
- Question 229: A developer has created an application based on customer req...
- Question 230: Refer to the exhibit. An engineer creates a function that ga...
- Question 231: On which system must the messaging standards be defined to a...
- Question 232: An application must be able to print the values of the varia...
- Question 233: What is a benefit of continuous tasting?...
- Question 234: Which database type should be used with highly structured da...
- Question 235: A developer must create VLANs 2-5 on a remote Cisco NX-OS sw...
- Question 236: A developer releases a new application for network automatio...
- Question 237: A developer is working on a bug fix. The existing branch nam...
- Question 238: Drag and Drop Question An engineer is trying to modify infor...
- Question 239: Refer to the exhibit. An engineer is implementing the respon...
- Question 240: When considering data privacy and security, which initial st...
- Question 241: Drag and Drop Question Drag and drop the code snippets from ...
- Question 242: An eCommerce company deployed a new web store application to...
- Question 243: What is the purpose of configuring NTP servers with the same...
- Question 244: Drag and Drop Question Refer to the exhibit. Drag and drop t...
- Question 245: Refer to the exhibit. An Intersight API is being used to que...
- Question 246: Refer to the exhibit. The Python code manages a Cisco CSR 10...
- Question 247: Refer to the exhibit. Which key value pair from the ios_ntp ...
- Question 248: A developer must apply a new feature on a live project. Afte...
- Question 249: The access token for a Webex bot has been stored in an envir...
- Question 250: On a Cisco Catalyst 9300 Series Switch, the guest shell is b...
- Question 251: What is a capability of end-to-end encryption when building ...
- Question 252: Cisco sensorBase gathers threat information from a variety o...
